Penetration Testing Reports, Guides, and Practical
Knowledge
Use these insights and resources to prepare for your next engagement, evaluate a vendor against real standards, or simply understand what attackers are doing right now.
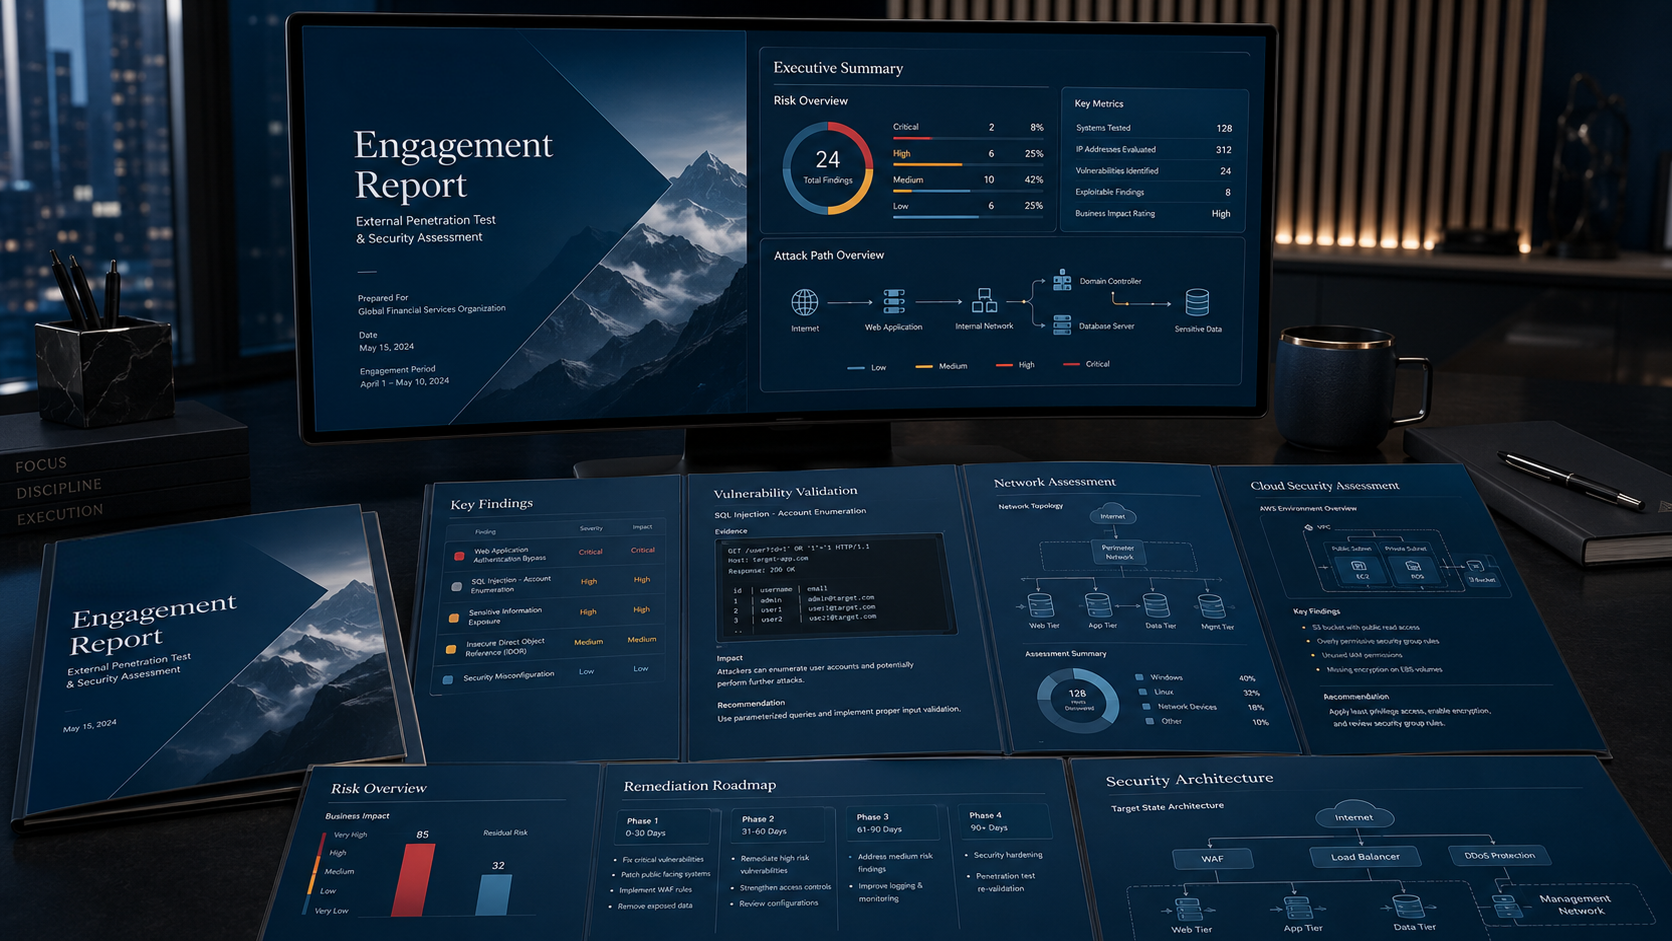
This is what a client receives at the close of an engagement, all three reports, identifying details removed. Structure, scoring, and remediation guidance are exactly as delivered.
Your board needs to understand exposure. Your security team needs to fix it. Your auditors need proof it happened. The Risk Impact Brief, the Technical Pentest Report, and the Attestation Letter deliver all three, from the same engagement.
- Executive summary with risk posture overview
- Critical and high severity vulnerabilities with CVSS scoring
- Steps to reproduce, with proof-of-concept evidence
- Remediation path for every vulnerability
- Compliance control mapping throughout
Actionable Insights
View all posts
Explore the Issues Behind the Test
Go deeper into the risks, attack paths, and testing decisions that shape a strong penetration testing program.

Standard pen testing can miss the risks unique to pharma. Explore how GxP, 21 CFR Part 11, third-party access, and nation-state threats change what belongs in scope.

AI can accelerate asset discovery, vulnerability correlation, attack-path modelling, and reporting. Explore where it helps testers move faster and where human judgment still matters.

Connected industrial environments create attack paths across IT, remote access, vendors, cloud, and the plant floor. Explore what CISOs need to test, scope, and defend.
Explore More Insights From DivIHN
Explore perspectives on security testing, compliance, risk, and the challenges organizations face in today's threat landscape.
A complete guide to mobile application penetration testing. Discover how security experts test iOS and Android apps to identify vulnerabilities and prevent data breaches.
R&D and GxP regulated environments have different risk profiles, compliance requirements, and testing constraints. Learn why a single unified pen test scope fails both and how to run dual-scope engagements efficiently.
Annual penetration testing produces documentation, not security. Learn how Penetration Testing as a Service fits manufacturing's high-change OT environments and closes the gap between discovery and fix.
Ransomware operators target the IT-OT boundary deliberately and they know manufacturing economics well. Learn how attackers pivot from IT into OT systems and what penetration testing finds before they do.
Don't wait for an auditor to tell you what you missed. Learn how to build an OT attack surface map using passive discovery, zone mapping, and risk-based prioritization before your next security audit.
Get Actionable Intelligence Straight From Penetration Testers
Get insights, threat updates, and resources matched to your role and priorities. Everything we publish, relevant to you, straight to your inbox.