Mobile Application Penetration Testing Services
Your mobile application is more than an interface; it's a direct connection to your customers, data, and business. Our methodology evaluates how attackers could compromise your Android and iOS applications by testing authentication, local data storage, APIs, business logic, and runtime security to identify exploitable vulnerabilities before they put your users or organization at risk.
A Mobile Application Is Only as Secure as Its Weakest Layer
Unlike web applications, mobile apps operate on devices you don't control, communicate over public networks, and often store or process sensitive information locally. Attackers can reverse engineer applications, tamper with binaries, intercept insecure communications, or exploit weaknesses in authentication and APIs that automated security scans frequently miss.
Mobile application security risks are not theoretical. A July 2025 study from Guardsquare and Enterprise Strategy Group found that 62% of surveyed organizations had experienced a mobile app breach in the previous year, with affected organizations reporting an average of nine breaches. This highlights why testing needs to look beyond automated scanning and examine how attackers could interact with the application, device, and backend services.
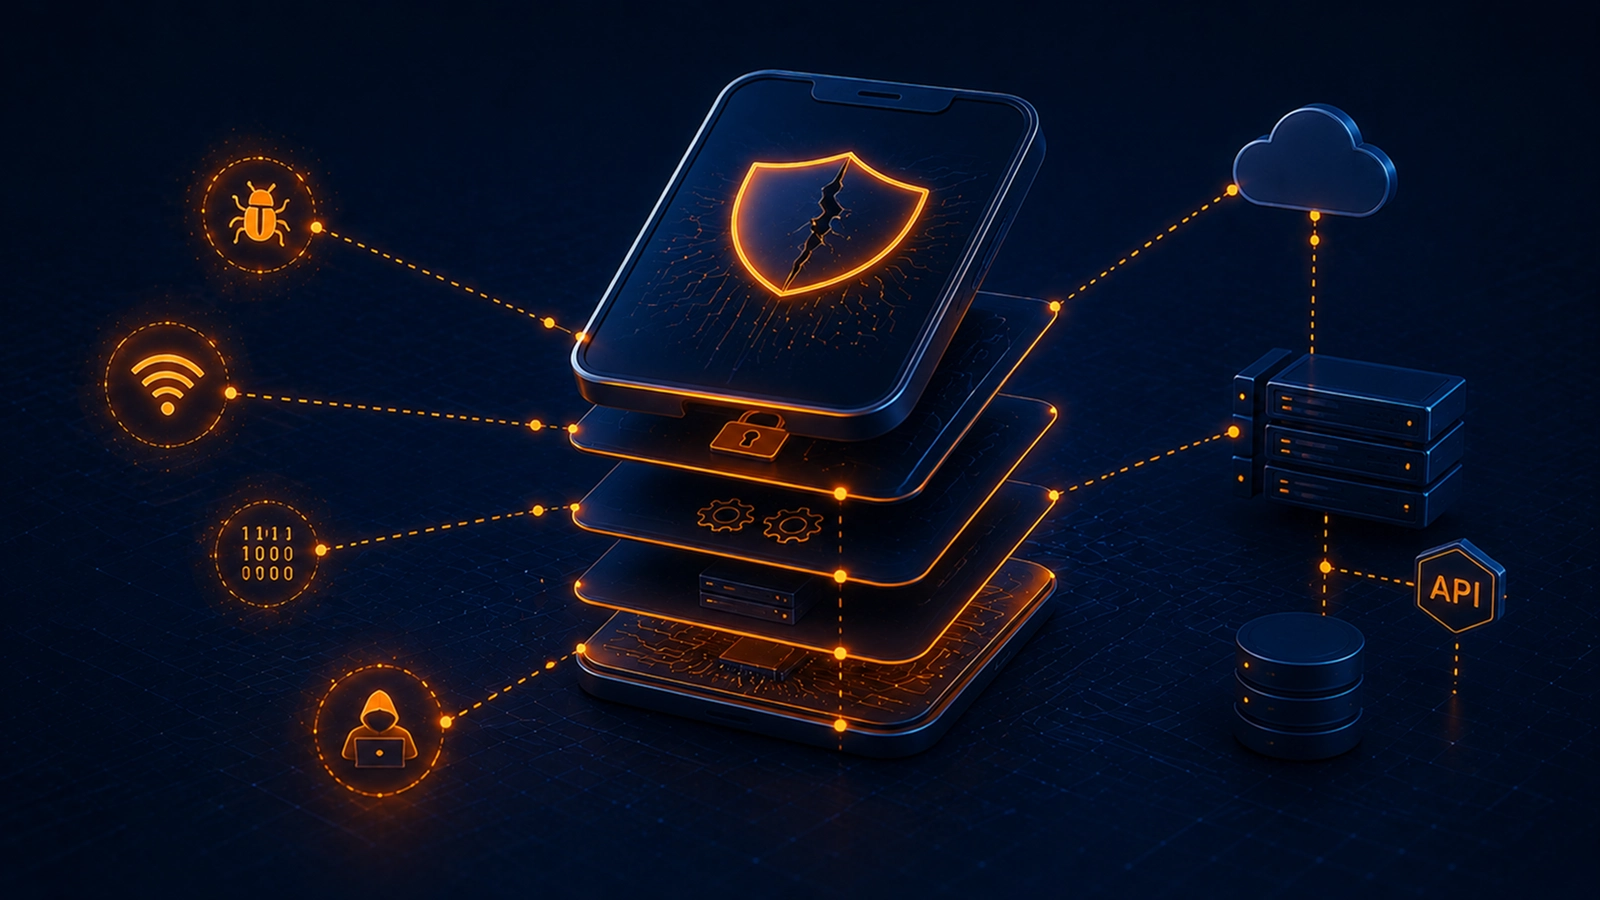
Measure Your App's Security at Every Layer

Check the App Inside Out
We review your Android and iOS applications for weaknesses such as insecure code, risky permissions, vulnerable third-party components, and hidden flaws that attackers could use to get inside your app.

Keep Customer Data Safe
From local storage and encryption to key management and secure communications, we identify weaknesses that could expose sensitive customer or business information.

Secure Every Connection
We evaluate API communication, authentication, authorization, and data exchange between your mobile application and backend services to uncover vulnerabilities beyond the device.

Test It Like an Attacker
We test how your Android and iOS applications hold up against real attack techniques such as rooted or jailbroken devices, runtime tampering, and attempts to bypass the controls that protect your data.
Mobile Application Security Evaluation Toolkit
Everything Delivered with Your Mobile Security Assessment

Penetration testing runs on physical Android and iOS devices, surfacing platform-specific risks across device controls, runtime behavior, authentication, and local storage that emulators typically miss.

Every validated finding includes technical evidence, business impact, and practical remediation recommendations, enabling development and security teams to prioritize and resolve issues with confidence.

After a Critical or High finding has been addressed, we perform a retest at no additional cost to verify that the vulnerability has been remediated and the security improvement is effective before the next release.
Protect Every Update Before It Reaches Your Users
Every mobile application evolves through new features, operating system updates, third-party SDKs, API enhancements, and performance improvements. While these changes drive innovation, they can also introduce new vulnerabilities that place customer data, business operations, and brand reputation at risk if left untested.
Our mobile application penetration testing methodology helps you validate every major release before it reaches production. By identifying security weaknesses introduced through new functionality, backend integrations, or platform updates, your team can release Android and iOS applications with greater confidence while reducing the risk of exploitable vulnerabilities reaching your users.
What Teams Ask Before Testing Their Mobile App
Which parts of a mobile application are evaluated during testing?
A mobile application penetration test evaluates Android and iOS applications for vulnerabilities in authentication, authorization, local data storage, encryption, API communication, session management, runtime behavior, reverse engineering resistance, and business logic. Senior testers manually validate every finding.
Do you test both Android and iOS applications?
Yes. Our methodology supports security assessments for both Android and iOS applications, evaluating platform-specific risks alongside vulnerabilities that affect shared application logic, APIs, and backend communication.
Does your methodology follow OWASP MASVS and MASTG?
Yes. Our mobile application penetration testing methodology uses the OWASP Mobile Application Security Verification Standard (MASVS) to evaluate the security controls an application should meet and the OWASP Mobile Application Security Testing Guide (MASTG) to guide testing of those controls across Android and iOS applications.
Why isn't automated mobile security testing enough?
Automated security testing can identify known vulnerabilities and configuration issues, but it may miss business logic flaws, insecure runtime behavior, authentication weaknesses, reverse engineering risks, and chained attack scenarios. Manual penetration testing evaluates how these weaknesses could be exploited together in realistic attack scenarios.
Will you test the APIs used by our mobile application?
Yes. Mobile application security extends beyond the app itself. Our methodology evaluates API authentication, authorization, input validation, session handling, and data exchange to identify vulnerabilities that could expose sensitive information or backend services.
At what stage of development should mobile security testing begin?
Start security testing during development, once your app's core features, login flow, and API connections are in place. Testing at this stage lets your team fix weaknesses while changes are still quick and inexpensive, before the app goes through store review and reaches users. A final round before your first production release confirms the app is ready to launch.
Will the final report include remediation guidance?
Yes. Every validated finding includes technical details, business impact, proof-of-concept where applicable, risk prioritization, and practical remediation recommendations to help development and security teams resolve issues efficiently.
How often should a mobile application be penetration tested?
Plan a full penetration test at least once a year. Add a focused test whenever your app changes in a meaningful way, such as a major feature release, a new third-party SDK, an API update, or a significant iOS or Android update. Because mobile apps ship updates often, building testing into your release calendar keeps your security in step with every version your users download.