Penetration Testing Services for Healthcare
Every system that touches electronic protected health information (ePHI) carries regulatory weight beyond typical IT risk. A certified penetration tester scopes testing to the systems and access paths that touch patient data, and maps every vulnerability to the exact CFR section a HIPAA auditor evaluates.
ePHI Systems Carry Risks a Standard Scan Won't Map to Your Regulatory Requirements
A vulnerability scan finds open ports and outdated software. It doesn't connect those findings to 164.308(a)(8), 164.310, or 164.312, the specific CFR sections an auditor or OCR reviewer actually evaluates. That gap leaves your compliance team translating technical output into regulatory language on their own.
Electronic health record systems, patient portals, and connected medical devices each touch ePHI differently, and each carries its own exposure. Testing scoped to these systems specifically shows where patient data is actually reachable, not just where a generic scan happened to point.
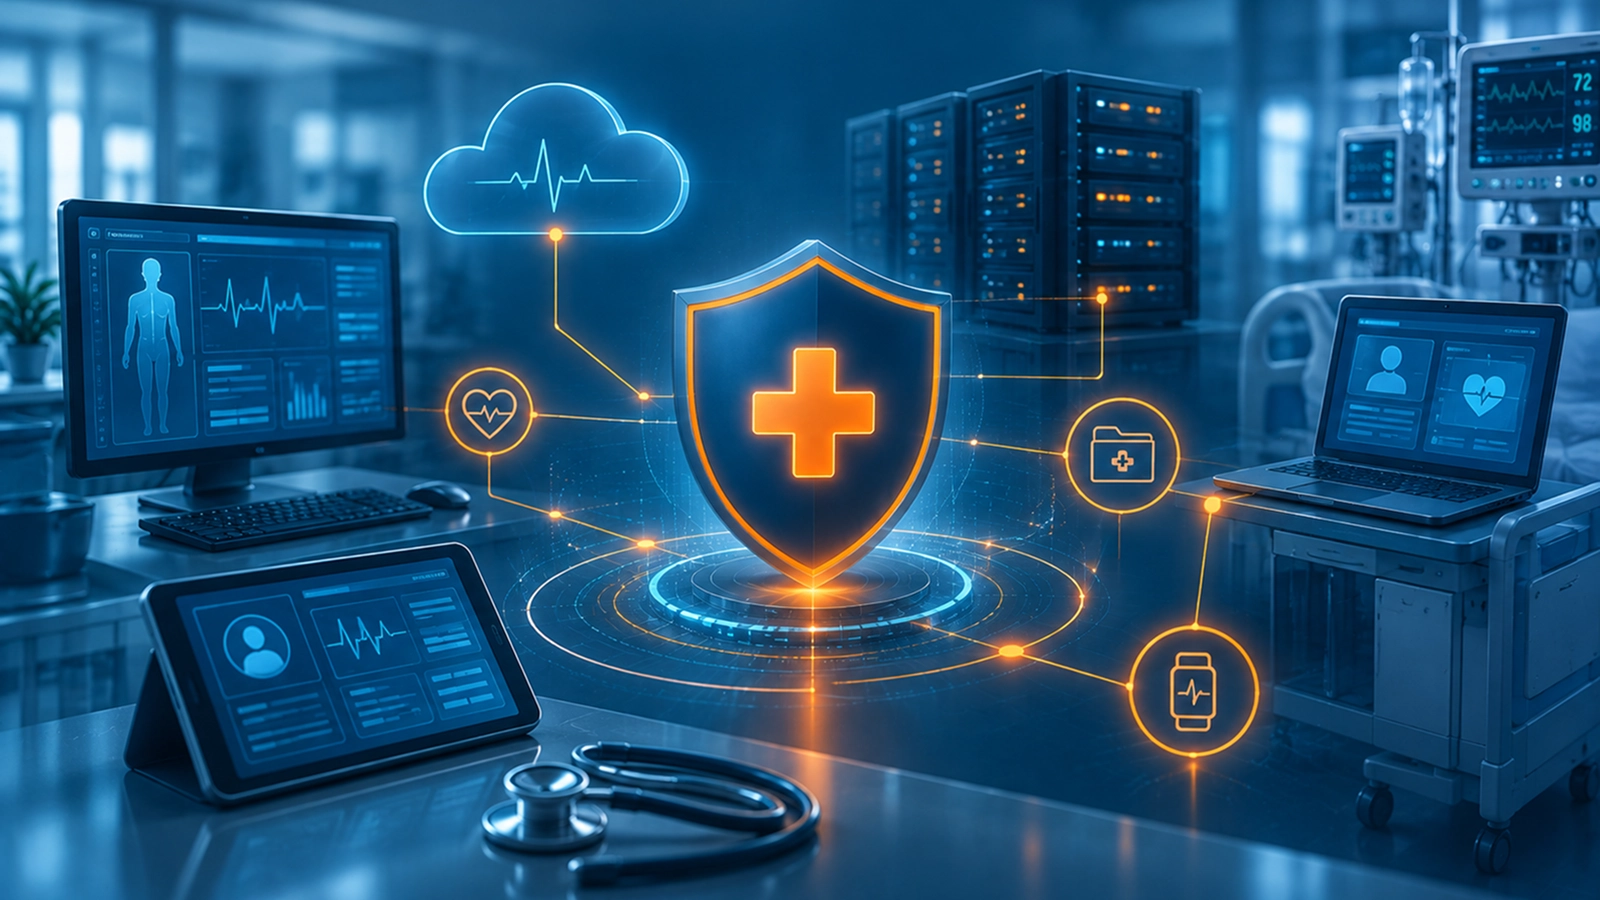
Where Patient Data Actually Lives

Electronic Health Record Systems
Your EHR platform sits closest to ePHI exposure, so testing pushes on its access controls and authentication paths first.

Patient Portals and Web Applications
Portals put ePHI one login away from the public. Testing targets the vulnerability classes that could expose it to an unauthorized user.

Connected Medical Devices
Testing follows each networked medical device to see whether its network connection opens a path into broader systems.

Business Associate Connections
How far can a vendor's access reach? Testing measures what each third-party integration touching ePHI exposes in your environment.
Know What the Proposed HIPAA Rule Would Change
Evidence Your Compliance Team Can Use Directly

Annual testing today already matches what the proposed HIPAA Security Rule would require, so your team stays ready whether the final rule publishes this year or next.

Vulnerabilities arrive cited alongside the exact CFR section they map to, so your compliance team hands the report over without translating technical findings into regulatory language first.

Remediation evidence feeds directly into your HIPAA risk analysis documentation, supporting the ongoing risk management process 164.308(a)(1) already requires.
A Report Organized the Way Auditors Read
The final report goes beyond flagging issues. Each finding sits next to the specific CFR section it maps to, 164.308(a)(8), 164.310, or 164.312, organized section by section, the same way auditors review the rule.
The engagement delivers a Risk Impact Brief for leadership, a Technical Pentest Report for your compliance and security teams, and an Attestation Letter any auditor can review directly.
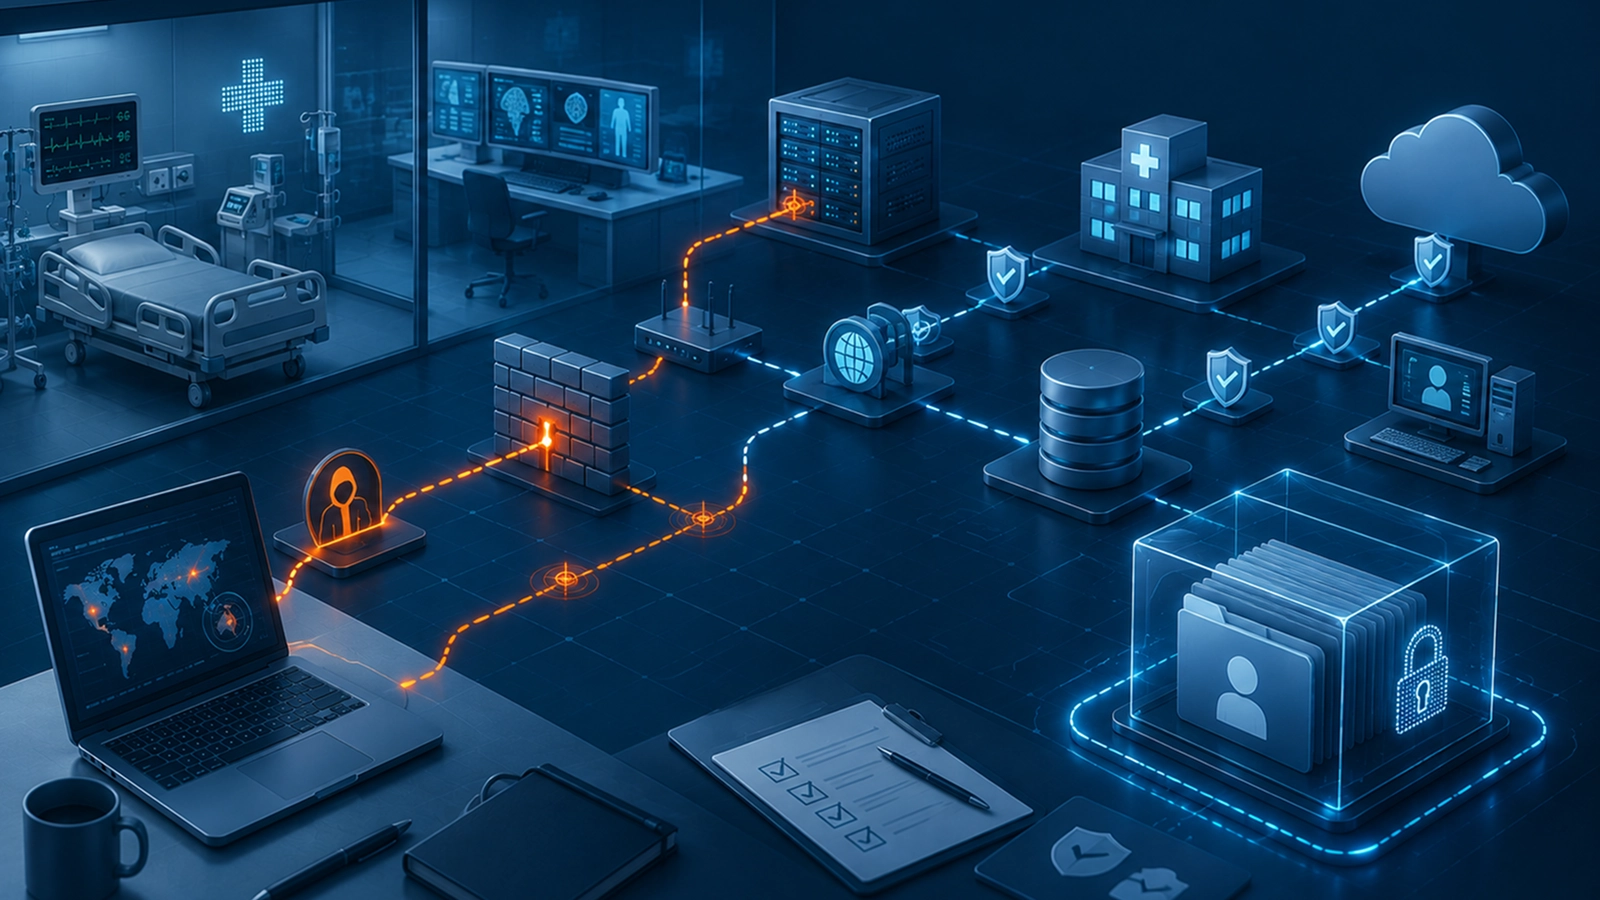
What to Know Before Testing Healthcare Systems
Does testing map directly to HIPAA requirements?
Yes, testing maps every vulnerability to 164.308(a)(8), 164.310, or 164.312, the specific CFR sections a HIPAA auditor evaluates, and the report cites the regulation alongside each finding.
Is penetration testing currently required under HIPAA?
Not yet as a standalone mandate. HHS's proposed 2025 Security Rule update would require penetration testing at least once every 12 months and vulnerability scanning at least every six months, performed by a qualified person, codified at 45 CFR 164.312(h). That rule remains proposed, not finalized.
Who owns the report and the underlying data after the engagement ends?
Your organization owns the final report and all findings from the engagement. Testers handle any ePHI encountered during testing under the data handling terms your team confirms before testing begins, and securely return or destroy all engagement data at close, following the retention period set in your agreement.
How does this feed into our HIPAA risk analysis?
Remediation evidence feeds directly into your existing risk analysis documentation, supporting the ongoing risk management process 164.308(a)(1) requires.
Does the engagement include a retest?
Yes, every engagement includes one retest of Critical and High findings at no additional cost. Once your team reports the fix, a tester checks it inside the retest window set at kickoff.
Will testing disrupt systems supporting live patient care?
Testing methods match what each system can safely absorb, and any system supporting live patient care receives non-disruptive methods only.
How is patient data handled if testers encounter it during testing?
Your team and the testers confirm ePHI data handling terms before testing begins, covering exactly how testers handle, store, and report any patient data they encounter.