Penetration Testing Services in Illinois
Find the security weaknesses across your Illinois environment before an attacker or auditor does. Senior penetration testers shape every engagement around your systems and deliver practical findings that cut risk across applications, networks, cloud, and business-critical systems.
A Generic Vulnerability Scan Won't Tell You What an Attacker Actually Sees
As organizations across Illinois continue adopting cloud platforms, third-party services, hybrid infrastructure, and remote access technologies, their attack surface becomes increasingly complex. Although automated vulnerability scans can identify known weaknesses, they cannot demonstrate how multiple vulnerabilities could be combined to compromise business systems, applications, or sensitive information.
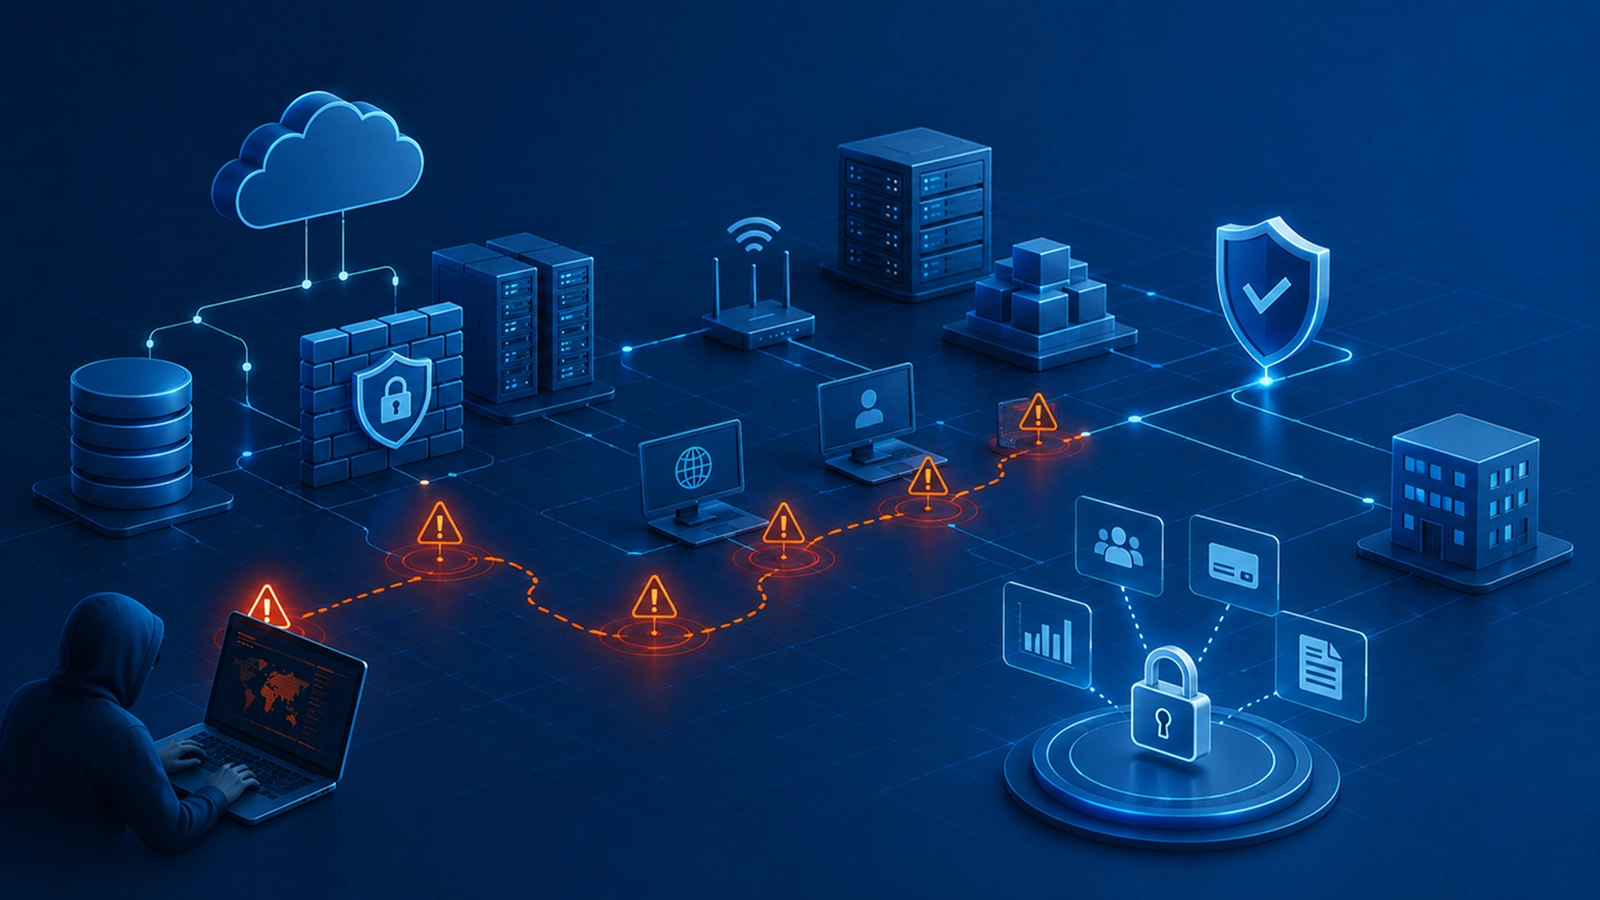
Completing a penetration test solely to satisfy compliance requirements does not reveal how an attacker could move through your environment, target business-critical assets, or gain access to sensitive customer data. Manual penetration testing provides the attacker's perspective needed to validate real-world risk before it results in a security incident.
Evaluate the Systems That Matter Most to Your Business

Gain Visibility Across Your Attack Surface
Understand how an attacker could move across your internal network, cloud infrastructure, remote access points, and connected environments before they become opportunities for compromise.

Secure Critical Business Applications
Testing targets your customer-facing portals, internal applications, and APIs for vulnerabilities that could expose sensitive data, disrupt operations, or impact business continuity.

Assess Cloud Security Configurations
Identify cloud misconfigurations, excessive permissions, and exposed services that attackers could use to access workloads, data, or connected business systems.

Validate Remote Access and Identity
VPNs, remote desktop, single sign-on, and privileged accounts give attackers a direct way in. Testing shows how far one compromised login could reach across your environment.
Choose the Right Penetration Testing Partner
Three Things You Get on Every Engagement

Senior penetration testers with hands-on enterprise experience lead every assessment and validate every finding against real attack techniques.

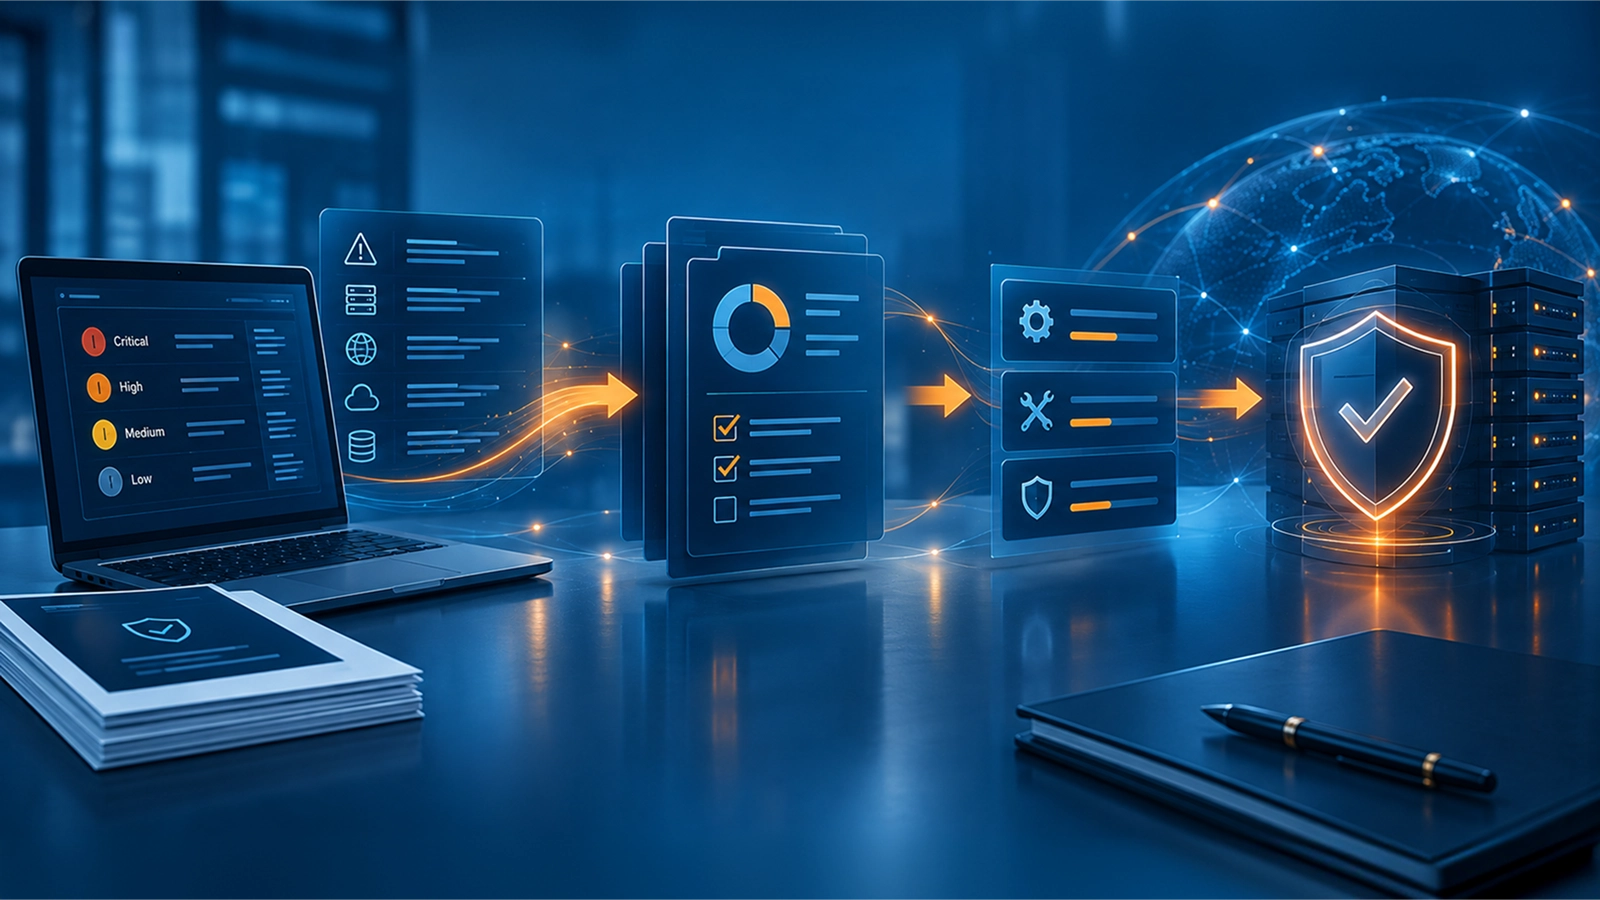
Leadership gets a Risk Impact Brief, your security team gets a Technical Pentest Report, and auditors and business partners get an Attestation Letter, each with business impact and clear remediation guidance.

Once your team remediates, testers retest Critical and High findings at no additional cost and confirm every fix holds before the engagement closes.
Security Improvements Start with Actionable Results
A penetration test pays off when findings turn into real improvements. Every engagement shows your team which vulnerabilities carry the most business risk, why they matter, and what to fix first.
Testers turn every finding into a clear, practical recommendation your security and IT teams can act on right away, with business impact spelled out. The result is a direct path from testing to measurable security gains.
What Illinois Teams Ask before Testing
How often should an organization perform a penetration test?
Most organizations should test at least annually and after significant infrastructure changes, application releases, cloud migrations, or major network modifications. Regular testing also helps maintain compliance and catch new security risks as your environment evolves.
What is included in a penetration testing engagement?
Every engagement includes reconnaissance, vulnerability validation, manual exploitation, risk analysis, detailed reporting, and remediation recommendations. Depending on your requirements, testing can cover networks, web applications, mobile applications, cloud environments, APIs, wireless infrastructure, and internal systems.
How is a penetration test different from a vulnerability scan?
A vulnerability scan automatically flags known weaknesses, while a penetration test proves exploitability through manual testing. That gives you a more accurate picture of business risk by uncovering attack paths, chained vulnerabilities, and security gaps that only hands-on testing reveals.
Will penetration testing disrupt business operations?
Your rules of engagement, testing boundaries, and stop points shape every test. Testers work closely with your stakeholders to keep operations running smoothly while still validating meaningful security risks. Where sensitive systems are involved, testing uses read-only checks and added safeguards.
Can penetration testing help with compliance requirements?
Yes, penetration testing supports regulatory, contractual, and security assessment requirements by identifying vulnerabilities and providing documented findings for remediation. For PCI DSS, Requirement 11.4 calls for internal and external penetration testing at least every 12 months and after significant changes to the cardholder data environment, with retesting after remediation. Every engagement follows recognized approaches, including NIST SP 800-115 and PTES.
How long does a penetration testing engagement take?
The duration depends on the size and complexity of your environment. Most engagements run two to four weeks, including planning, testing, reporting, and a final walkthrough of findings.
What does the final penetration testing report include?
Every engagement delivers three key deliverables: a Risk Impact Brief for leadership, a Technical Pentest Report for your security team, and an Attestation Letter for your auditor. Together, they provide business context, technical findings, supporting evidence, risk details, remediation guidance, and the formal documentation your team needs to act on the results.
What Illinois-specific security requirements should organizations plan around?
Illinois organizations should plan around requirements for reasonable data security, vendor relationships, and protection of sensitive information. The Illinois Personal Information Protection Act (PIPA) sets requirements for reasonable security measures and for contracts with vendors handling personal information, while the Biometric Information Privacy Act (BIPA) sets a standard of care for biometric information. A penetration test helps identify security weaknesses tied to these obligations, and testing supports them as one part of a broader security program.