Social Engineering Penetration Testing Services
A convincing phone call can bypass layers of technical defense. Testers run real phishing, vishing, and pretexting campaigns against your team, measuring click rates, verification behavior, and credential-sharing responses under pressure. Results break down by role and department, showing where awareness training can deliver the greatest impact.
Technical Defenses Don't Stop a Convincing Voice
Firewalls, MFA, and endpoint detection strengthen technical defenses, while social engineering targets the people operating within those defenses. A well-timed call to the help desk, a spoofed vendor email, or an urgent wire-transfer request can manipulate trusted workflows and create an opening for an attacker.
Awareness training helps, but most programs test knowledge in a classroom, while attackers test behavior under real pressure. A phishing email late on a Friday or a vishing call impersonating IT during an outage test what only real pressure reveals.
Behavior under Pressure, Not Just Awareness

Phishing Susceptibility by Role
Click rates vary widely by department. Finance and IT typically face more targeted attempts, and the results show exactly where that gap sits in your organization.

Vishing and Pretexting Campaigns
A phone call impersonating IT support or a vendor contact tests whether your team verifies identity before acting, beyond spotting a suspicious email.

MFA Fatigue and Bypass Testing
Multi-factor authentication stops most automated attacks. Social engineering targets the employee who approves a push because someone convinced them it was routine.

Executive Targeting Resilience
Leadership faces more sophisticated, better-researched attempts than the rest of the organization. This measures whether that extra scrutiny actually translates into caution.
Know How Attackers Impersonate Your Leadership
A Baseline You Can Actually Track

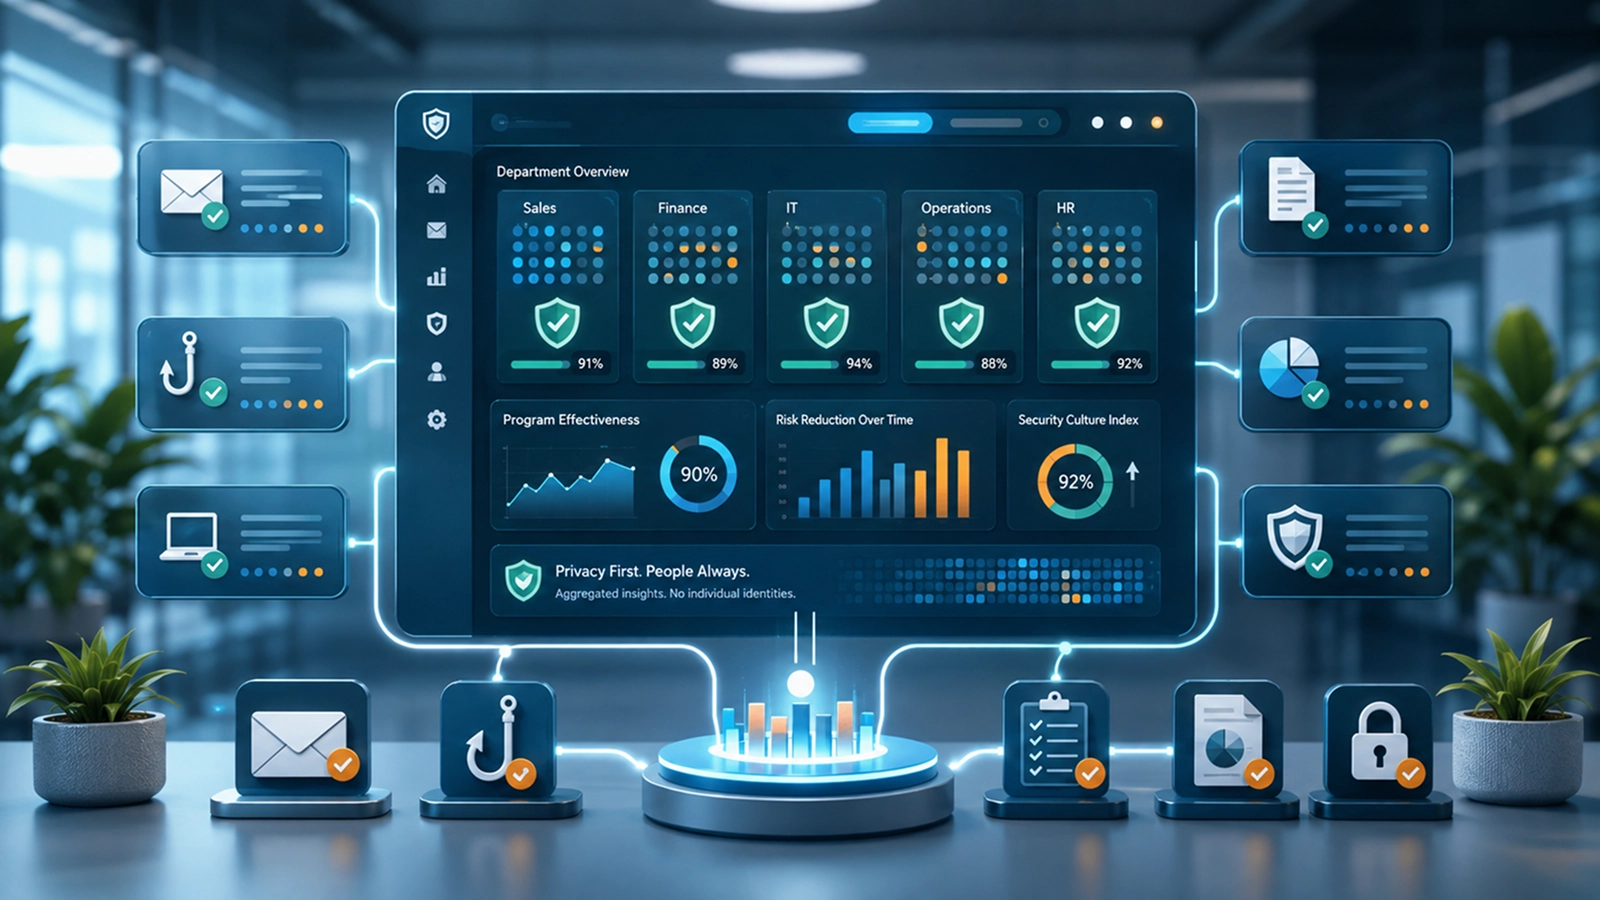
Click, callback, and MFA bypass results by role and department show exactly where awareness training will have the biggest impact, so you can put your training budget where it pays off most.

Click rates, callback rates, and MFA bypass rates translate human risk into a metric leadership can track quarter over quarter, the same way they track any other risk indicator.

Running the same style of campaign after training closes the loop, showing whether behavior actually changed showing whether behavior actually changed. This retest campaign is included at no additional cost.
Results Measure the Program, Not the Person
Every campaign runs with written approval from an executive sponsor, scoped with leadership sign-off before testing begins. Testing stays within work identity and professional context. Personal social media, family members, and off-hours activity are out of scope entirely.
Results get reported in aggregate, by role and department, not by naming individual employees who clicked. The goal is a stronger program, not a list of people to discipline.
What Leaders Ask before Testing Their Teams
Will employees know they're being tested?
Only your executive sponsor and the contacts named during scoping know in advance, and they approve the campaign in writing before it starts. The rest of your team receives no advance notice, so results reflect genuine behavior.
Are results tied to individual employees?
No. Results stay in aggregate, by role and department, with individual names kept out of every report.
Does this include phone-based testing, or just email phishing?
Yes, campaigns cover both. Testing includes phishing, vishing, and pretexting, so results reflect the full range of tactics attackers actually use.
Why do employees need to be tested if they've already had security awareness training?
Awareness training tests knowledge in a low-pressure setting. Real-world attempts test behavior under time pressure and social pressure, which training alone doesn't measure.
How long does a typical social engineering campaign run, one attempt or over several weeks?
A typical campaign runs over several weeks, spacing out phishing, vishing, and pretexting attempts the way a real attacker would. That spread gives a true read on susceptibility.
Who signs off on a social engineering engagement before it starts?
An executive sponsor approves the engagement in writing before any campaign runs. That approval sets which teams are in scope, which methods testers use, the testing window, and what happens if a targeted employee reports the attempt.