IoT Penetration Testing Services
IoT devices connect to your network but often sit outside your security team's visibility. A senior, certified penetration tester tests device firmware, credentials, and communication protocols for exploitable vulnerabilities, and delivers a report mapped to your compliance framework, with a retest included at no additional cost.
The Unwatched Devices Are the Ones Attackers Target First
Most security programs monitor servers, endpoints, and cloud workloads closely. IoT devices such as cameras, sensors, badge readers, and connected equipment get far less scrutiny after deployment. That gap is precisely where attackers look first, because an unreviewed device stays unnoticed when it's compromised.
Firmware ships with hardcoded secrets. Devices talk to each other over protocols with no encryption. Factory default passwords never get changed. Each of these becomes a foothold, and once an attacker has one, the question shifts from "is this device secure" to "what else on the network can it reach."
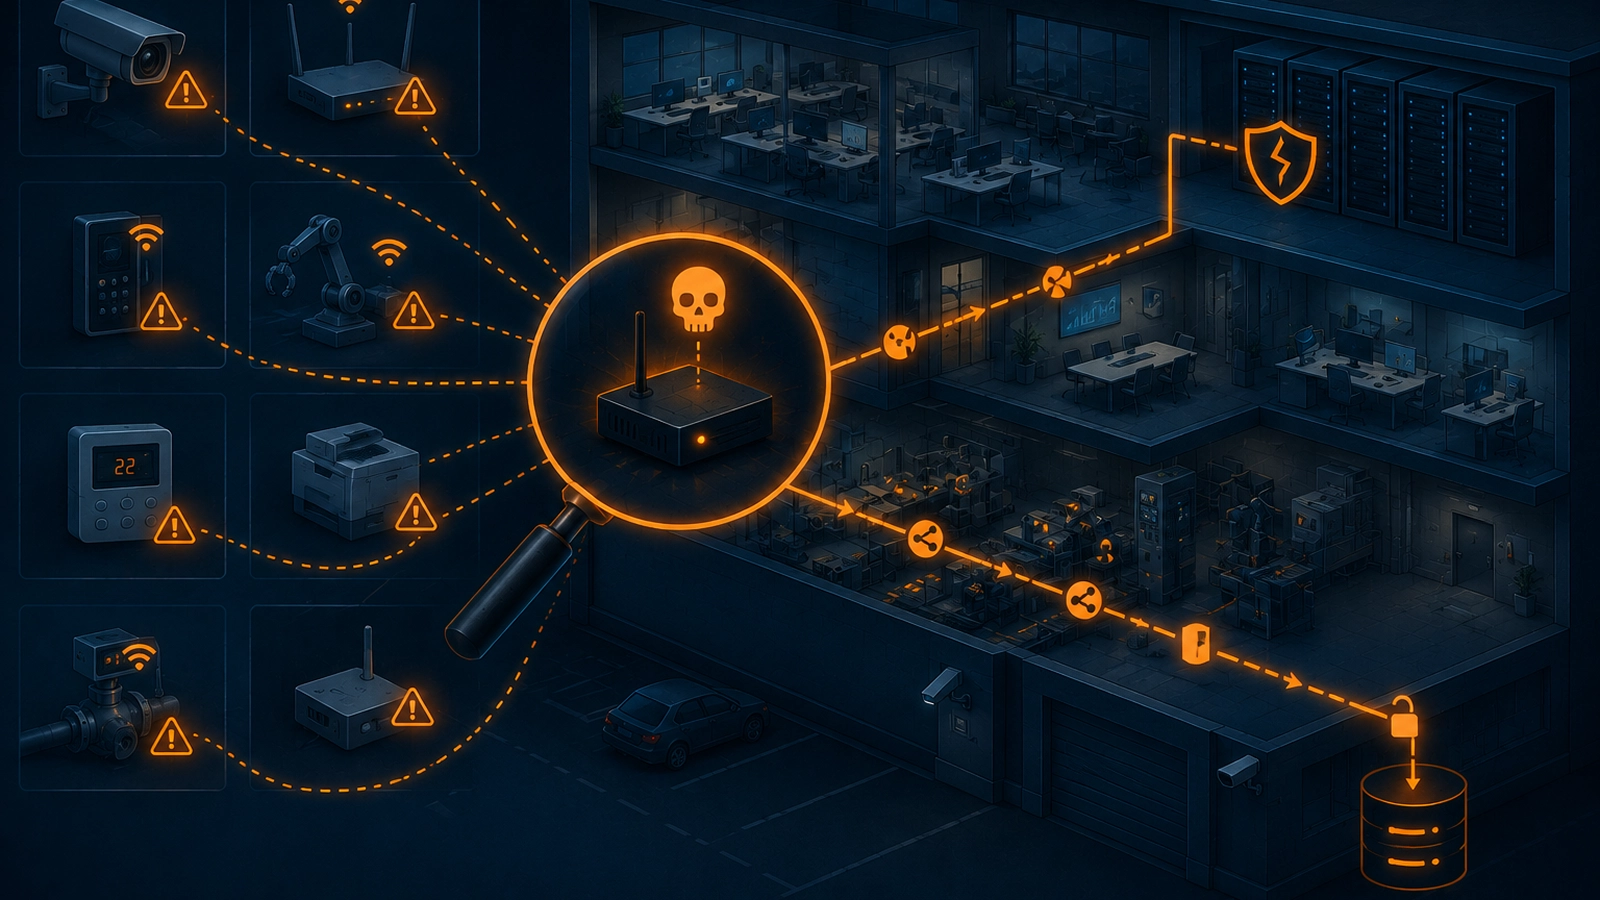
What an IoT Engagement Actually Involves

Firmware Reverse Engineering
A tester extracts and analyzes the device's firmware image directly, looking for hardcoded credentials, embedded keys, and backdoor access points that only hands-on analysis uncovers.

Device Communication Analysis
A tester captures and inspects real traffic between devices, checking whether data moves encrypted or sits exposed to anyone watching the network.

Physical Interface Testing
A tester examines the device itself, checking exposed debug ports and physical connectors that only a physical attacker can reach.

Default Credential Testing
A tester checks whether devices still run on out-of-the-box factory passwords, the most common way an IoT device gets compromised without any technical exploit at all.
Check Your IoT Exposure in Five Categories
Value Beyond the Vulnerability List

This engagement surfaces every connected device actually on your network, giving IT a verified inventory to compare against your asset management system.

Specific, documented vulnerabilities give your procurement team something concrete to bring to an IoT vendor during contract renewal or a security requirements discussion.

This engagement covers physical and network exposure together, so your team gets one complete set of findings.
Testing Live Devices While They Stay Up
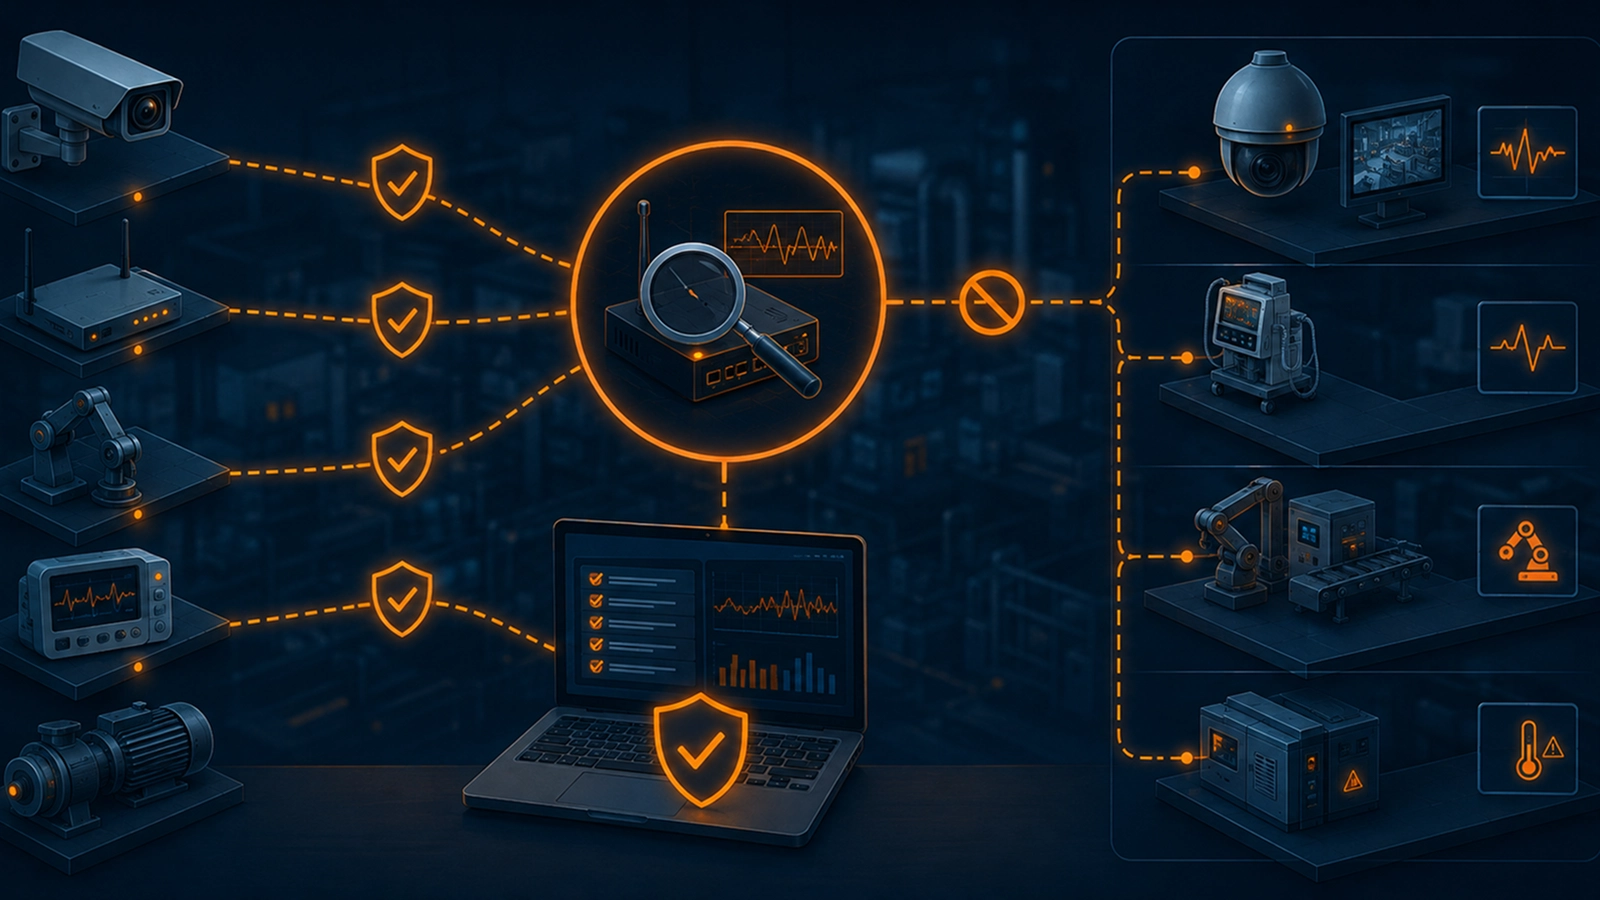
A misconfigured test against a production camera system, a hospital device, or a manufacturing sensor can cause real operational problems. IoT testing accounts for that risk from the start, using non-destructive methods on live devices and isolated analysis for anything that carries higher risk.
Devices that can't tolerate any interruption get flagged before testing begins, and your team decides together with the tester how to handle them, whether that means testing a duplicate unit, scheduling a maintenance window, or excluding it entirely.
What Teams Ask before an IoT Engagement
Is IoT testing different from a standard network penetration test?
Yes. IoT testing adds firmware reverse engineering, physical interface testing, and protocol-level traffic analysis, work that falls outside a standard external or internal network engagement.
Can our devices stay in production during testing?
Yes, devices that tolerate non-destructive testing stay live throughout the engagement. For devices that need zero interruption, testing moves to a duplicate unit or a scheduled maintenance window.
Is a retest included if we fix a vulnerability?
Yes, at no additional cost. Once your team reports the fix, a tester checks it inside the retest window set at kickoff.
Does the report map to our compliance requirements?
Yes. Every vulnerability ties to the specific control your framework requires, so your team can hand the report to an auditor without reformatting anything.
Does IoT testing support Cyber Resilience Act requirements?
Yes, for manufacturers selling connected products in the EU. The EU Cyber Resilience Act (Regulation (EU) 2024/2847) requires manufacturers to run regular security checks on connected devices and report actively exploited vulnerabilities and severe incidents to ENISA and their national CSIRT within 24 hours. The reporting duties have applied since September 11, 2026, and the wider rules follow on December 11, 2027. IoT testing produces the evidence those checks require.