Penetration Testing Services for Your Industry
Every organization runs on connected systems that attackers actively look for a way into, regardless of sector. Your business may need to protect customer data, financial records, intellectual property, or operational systems across internet-facing applications, cloud environments, remote access points, and internal networks. Our penetration testing services help you identify and validate exploitable security risks across your environment, giving your security and IT teams the insight they need to strengthen your defenses before an attacker finds the gap first.
Why Vulnerability Scanning Alone Isn't Enough
Attackers no longer rely mainly on stolen passwords to break in. Vulnerability exploitation now accounts for 31% of data breaches, the first time in nearly two decades that it has overtaken credential theft as the leading way attackers gain access, according to Verizon's 2026 Data Breach Investigations Report.
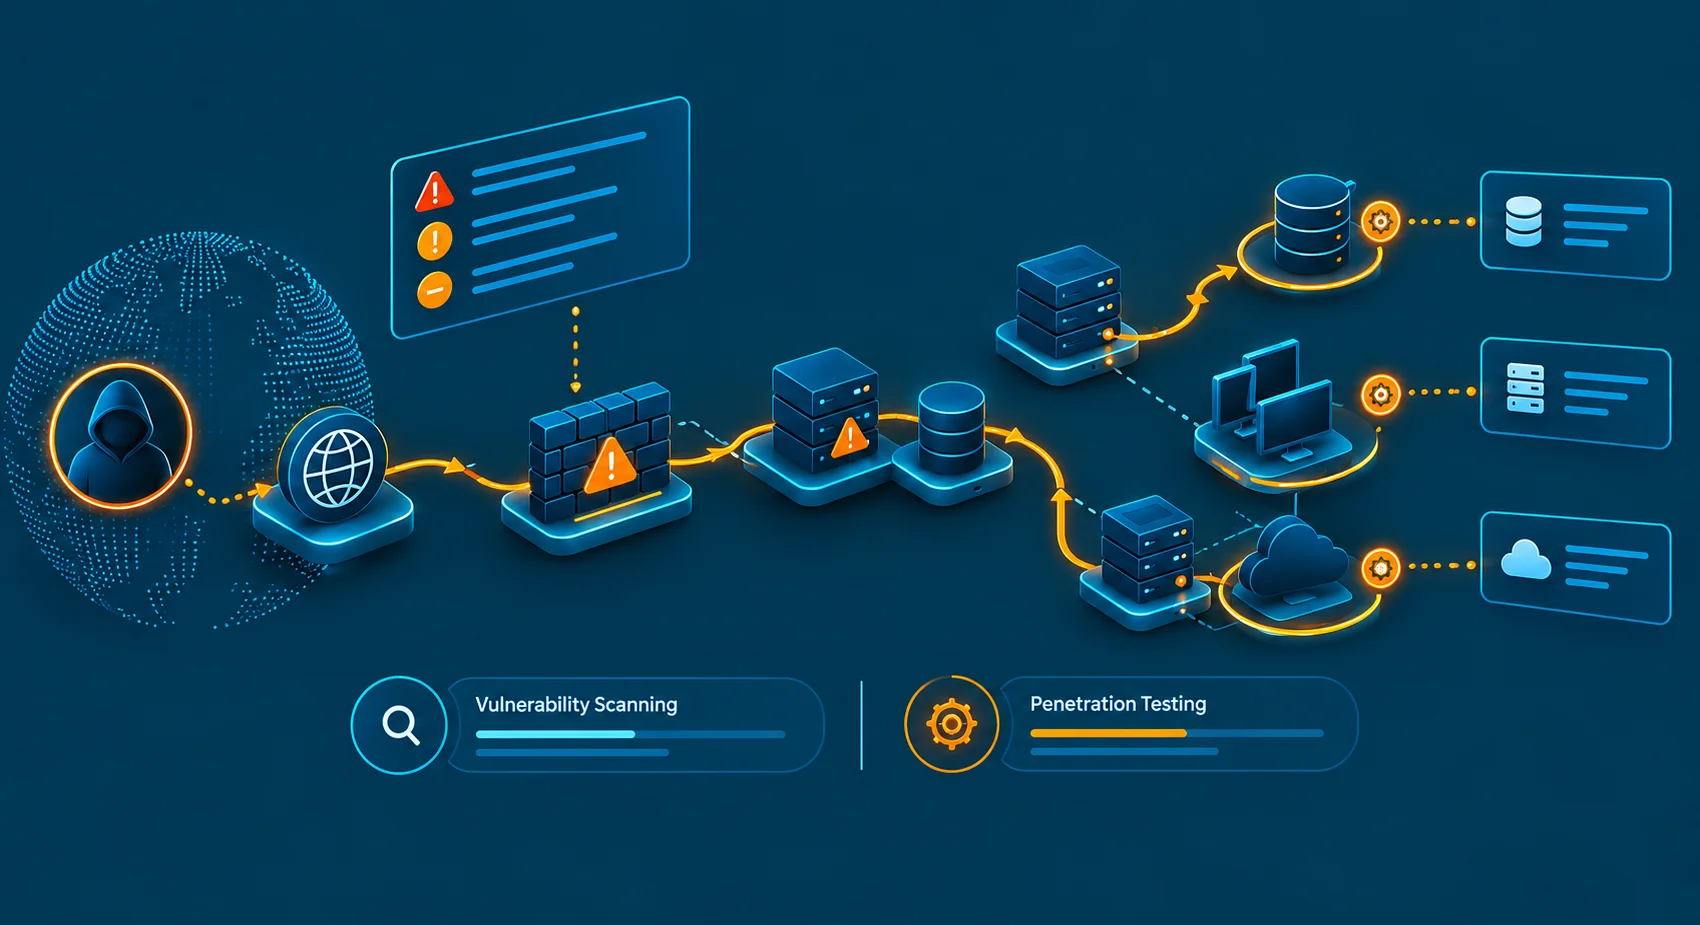
This shift means traditional vulnerability scanning alone may not give your team enough context to act. A penetration test validates whether an identified weakness can actually be exploited and shows how an attacker could move from that entry point toward your highest-value systems and data.
Secure the Systems That Keep Your Business Running

Protect Business-Critical Applications
We evaluate the applications, servers, and infrastructure your business depends on daily to identify vulnerabilities before they disrupt operations or expose sensitive data.

Assess Your Cloud and Digital Infrastructure
We review cloud environments, internal networks, and supporting infrastructure to identify security weaknesses across your organization's digital footprint.

Secure Third-Party and Vendor Connections
We validate the security of remote access, vendor integrations, and connected systems that could introduce risk into your environment from the outside in.

Prioritize Risks That Affect Your Operations
You receive actionable findings ranked by business impact, so your team can focus remediation efforts where they matter most to your organization.
Security Insights That Support Better Business Decisions

You'll understand which systems present the greatest business risk, allowing your security and IT teams to align remediation with your organization's priorities instead of treating every finding equally.

Every recommendation explains not only what to fix, but why it matters to your operations, your customers, and your organization's broader risk profile.

You leave the engagement with prioritized next steps, technical guidance, and the confidence to strengthen your security posture on your own timeline.
The Best Time to Find a Security Weakness Is Before an Attacker Does
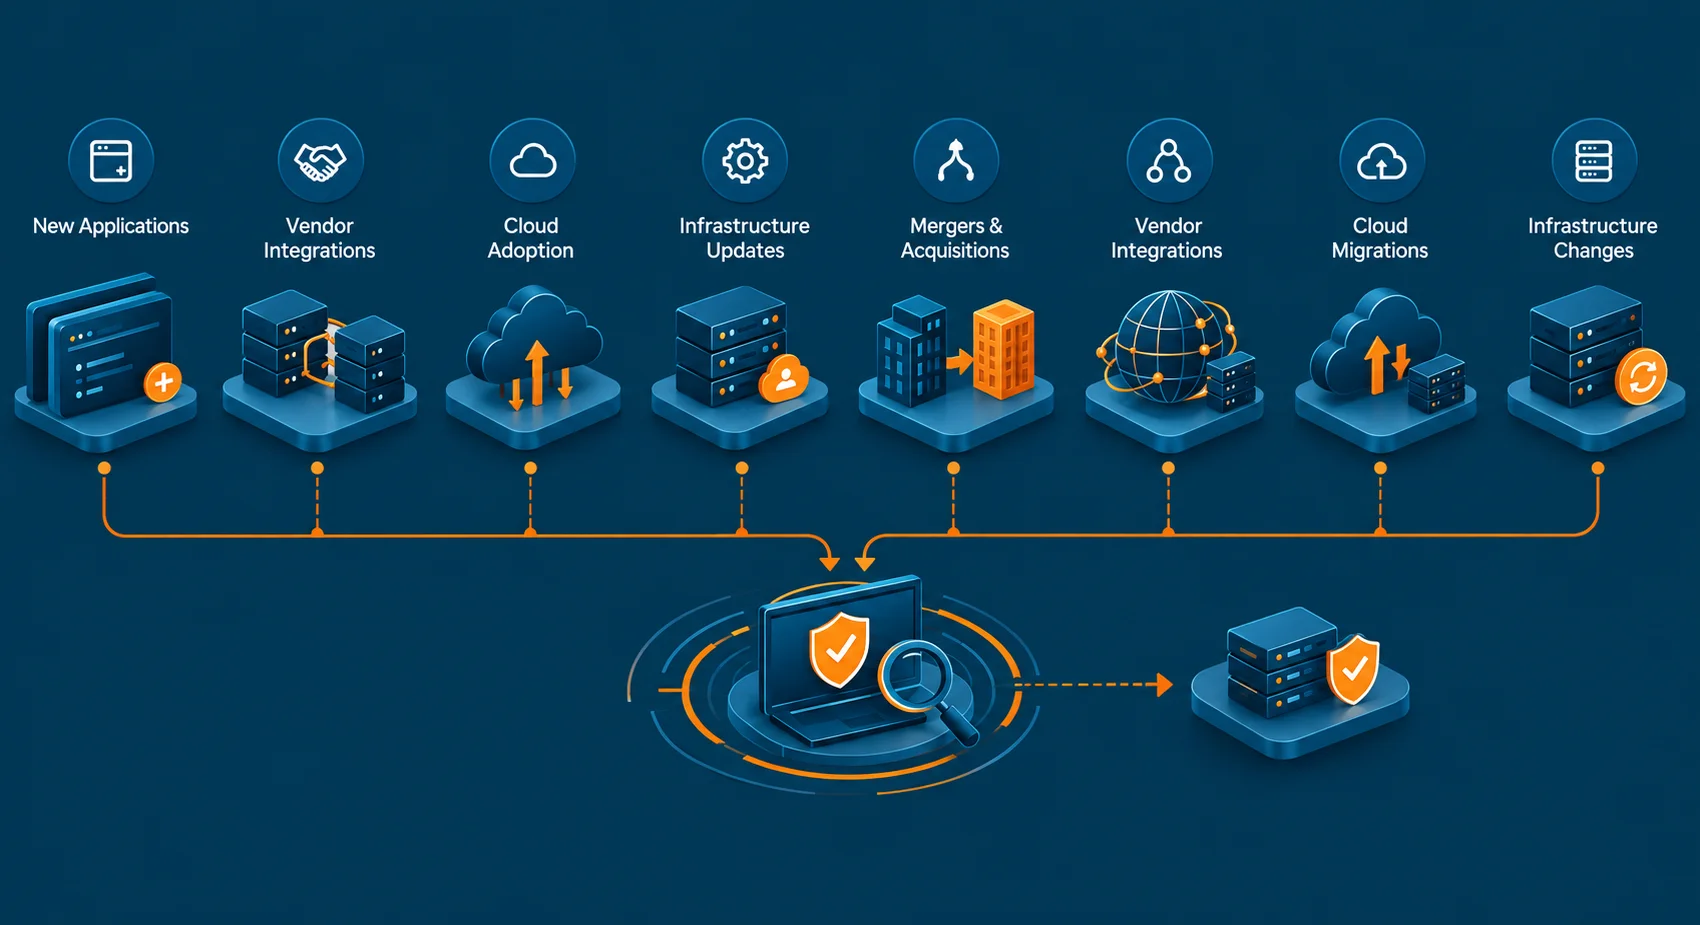
Your environment changes constantly through new applications, vendor integrations, cloud adoption, and infrastructure updates. Each change can introduce new security exposure.
Schedule penetration testing before major technology deployments, mergers or acquisitions, vendor integrations, cloud migrations, or significant infrastructure changes. Testing at these points gives your team the opportunity to identify exploitable weaknesses and address them before they affect your business.
What Teams across Industries Ask before Testing
Do you test organizations outside manufacturing, healthcare, and financial services?
Yes, testing covers government and public sector agencies, education, retail and e-commerce, technology and SaaS, legal and professional services, energy and utilities, and other sectors. Every engagement starts with a threat model built around how your sector operates.
Which compliance frameworks can testing support?
Testing maps findings to the frameworks your sector follows, including PCI DSS, SOC 2, ISO 27001, CJIS, FERPA, the GLBA Safeguards Rule, NIST frameworks, and IEC 62443. Your team confirms the applicable frameworks during scoping.
Can testing help with customer security questionnaires?
Yes, the Attestation Letter and Technical Pentest Report give your team current, independent evidence to answer customer questionnaires and vendor security reviews with confidence.
Does penetration testing support cyber insurance applications?
Yes, many insurers now ask for recent penetration test results during underwriting and renewal. The Attestation Letter gives you clear proof of testing to include with your application.
How does testing work for organizations with small IT teams?
Testing fits teams of any size. Your team names one main contact, testers handle the technical work, and every finding comes with step-by-step remediation guidance your team can follow on its own timeline.
What does the engagement deliver?
Every engagement delivers three reports. Leadership gets a Risk Impact Brief, your security team gets a Technical Pentest Report, and auditors and customers get an Attestation Letter, each with business impact and clear remediation guidance.
Does the engagement include a retest?
Yes, every engagement includes one retest of Critical and High findings at no additional cost, so your team gets verified proof each fix holds.
How long does a penetration testing engagement take?
Most engagements run [X to Y] weeks, depending on the number and complexity of systems in scope. Your team and the testers set the full timeline during scoping, so testing, reporting, and walkthroughs fit your schedule.
What should teams prepare before testing begins?
Your team should identify the systems in scope, share any compliance deadlines or audit dates, name a technical contact, and flag any operational constraints. That gives testers what they need to start fast.
What should our team prepare before a penetration testing engagement?
Your team should identify the systems to assess, define business priorities, nominate key technical contacts, and communicate any operational constraints that the testing team should consider during testing.
Who should be involved during a penetration testing engagement?
Successful engagements typically involve security teams, IT administrators, infrastructure owners, and application teams. Involving the right stakeholders helps streamline testing, validate findings, and accelerate remediation.