Wireless Network Penetration Testing Services
A wireless signal doesn't stop at your building's walls, and neither does the risk it carries. Wireless penetration testing evaluates encryption, authentication, rogue access points, and network segmentation from the same positions an attacker could use outside your facility.
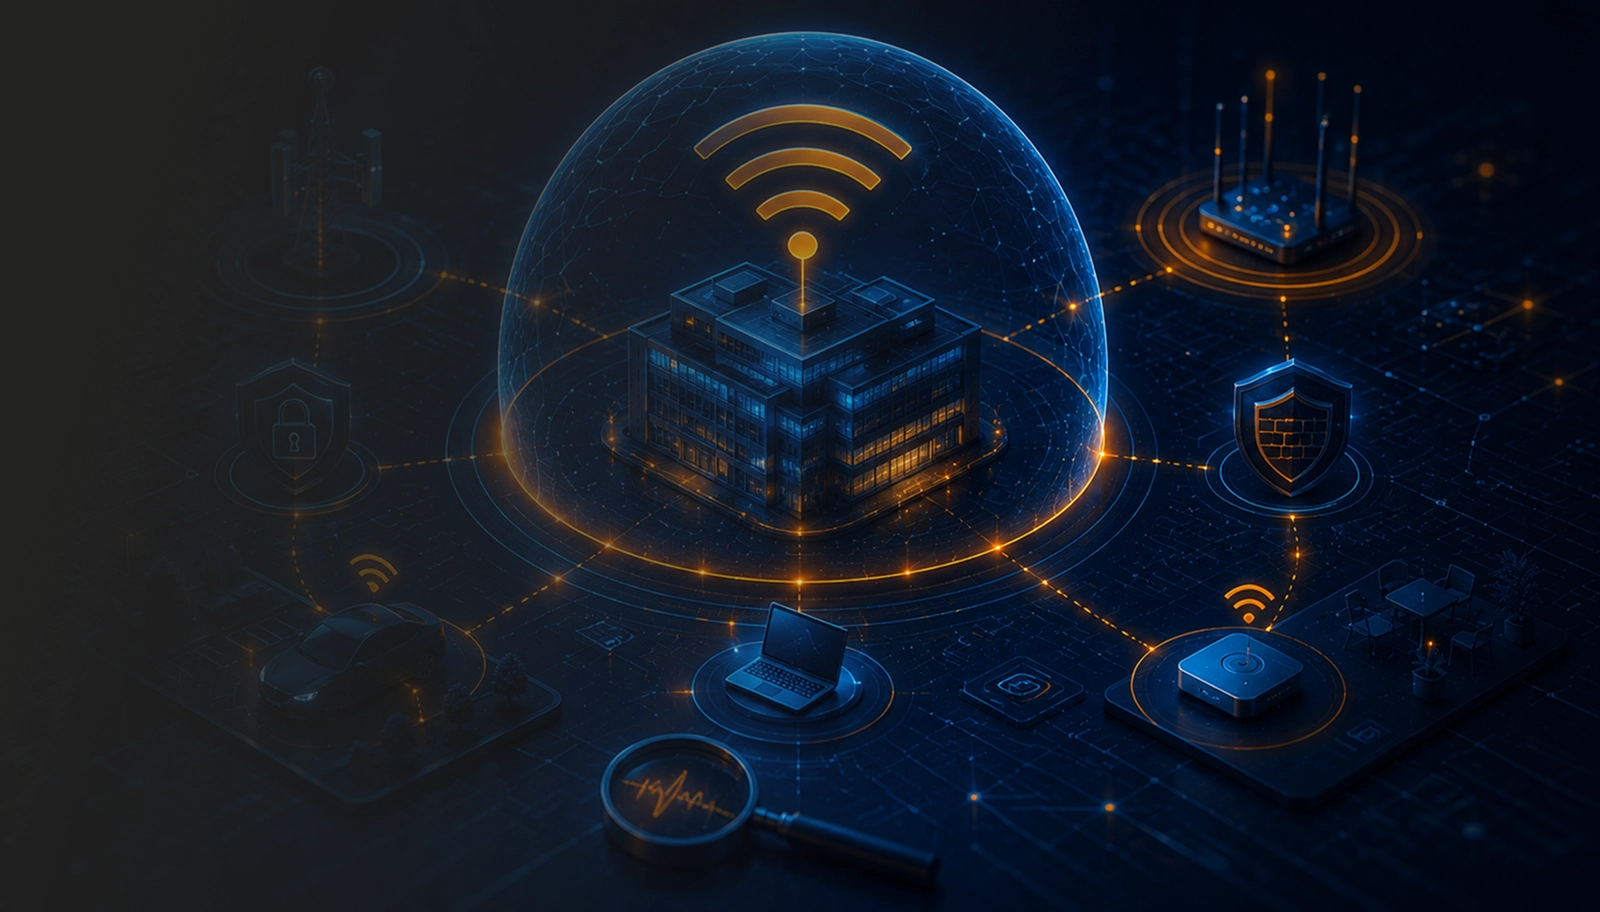
Anyone Within Range Is Already at Your Network's Edge
A firewall stops traffic at a defined boundary. Wireless signal has no such boundary. It reaches the parking lot, the floor above, the coffee shop across the street. Anyone within range of that signal is standing at the edge of your network, whether your security team accounts for that or not.
A rogue access point mimicking your network name, an evil twin capturing credentials from an unsuspecting employee, or a weak PSK cracked from a captured handshake each grant access without ever touching a single firewall rule. Testing evaluates exactly what's reachable from outside the building, not just what's visible on the network diagram.
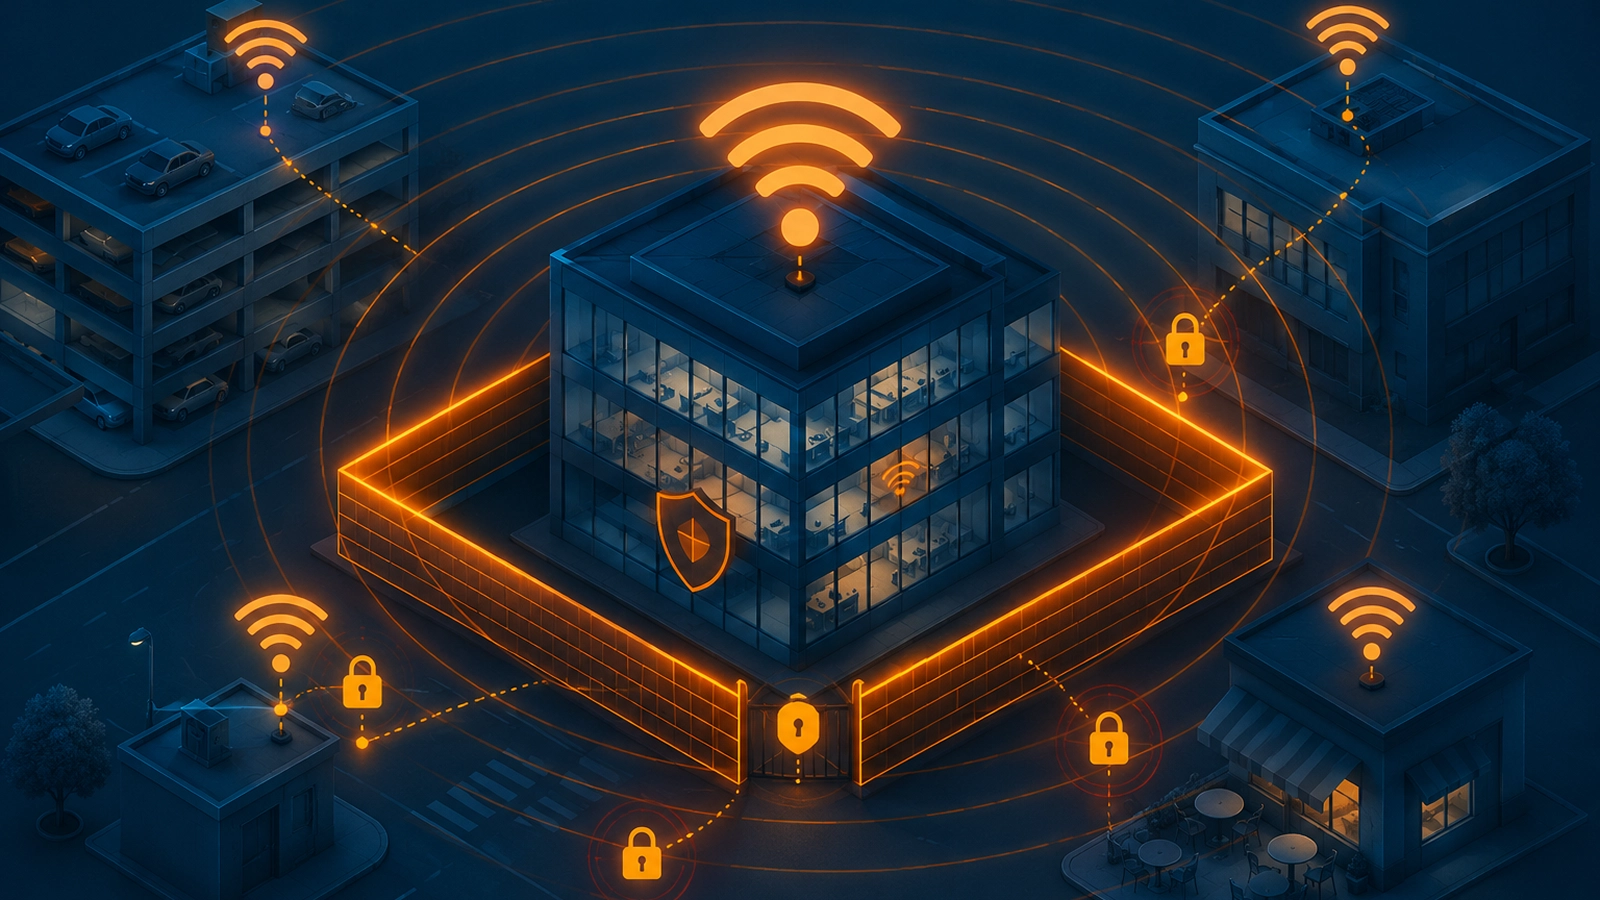
Four Places Wireless Risk Concentrates

Encryption and Authentication Testing
A tester assesses WPA2 configurations for resistance to handshake and PMKID-based credential attacks, and evaluates WPA3 transition-mode configurations for potential downgrade exposure when WPA2 compatibility remains enabled.

Rogue Access Point Detection
Unauthorized access points mimicking your network name get identified, along with whether your monitoring would catch one appearing today.

Guest Network Segmentation
Testing confirms whether guest traffic genuinely stays isolated from internal systems, or whether a misconfiguration provides a bridge between the two.

Wireless Client Attack Simulation
Evil twin setups and deauthentication attacks test whether employee devices can be tricked into connecting to an attacker-controlled network.
The First Five Minutes: Wireless Intrusion Response
Confidence That Outlasts the Engagement

Most teams assume guest network segmentation works. This engagement confirms it directly, rather than trusting a configuration nobody has tested since it was set up.

Every access point found during testing gets documented, giving your team a verified baseline of authorized devices to monitor against, so a new rogue AP stands out the moment it appears.

Signal boundary findings can inform access-point placement, facility design, RF containment, and shielding considerations for new offices or facility expansions.
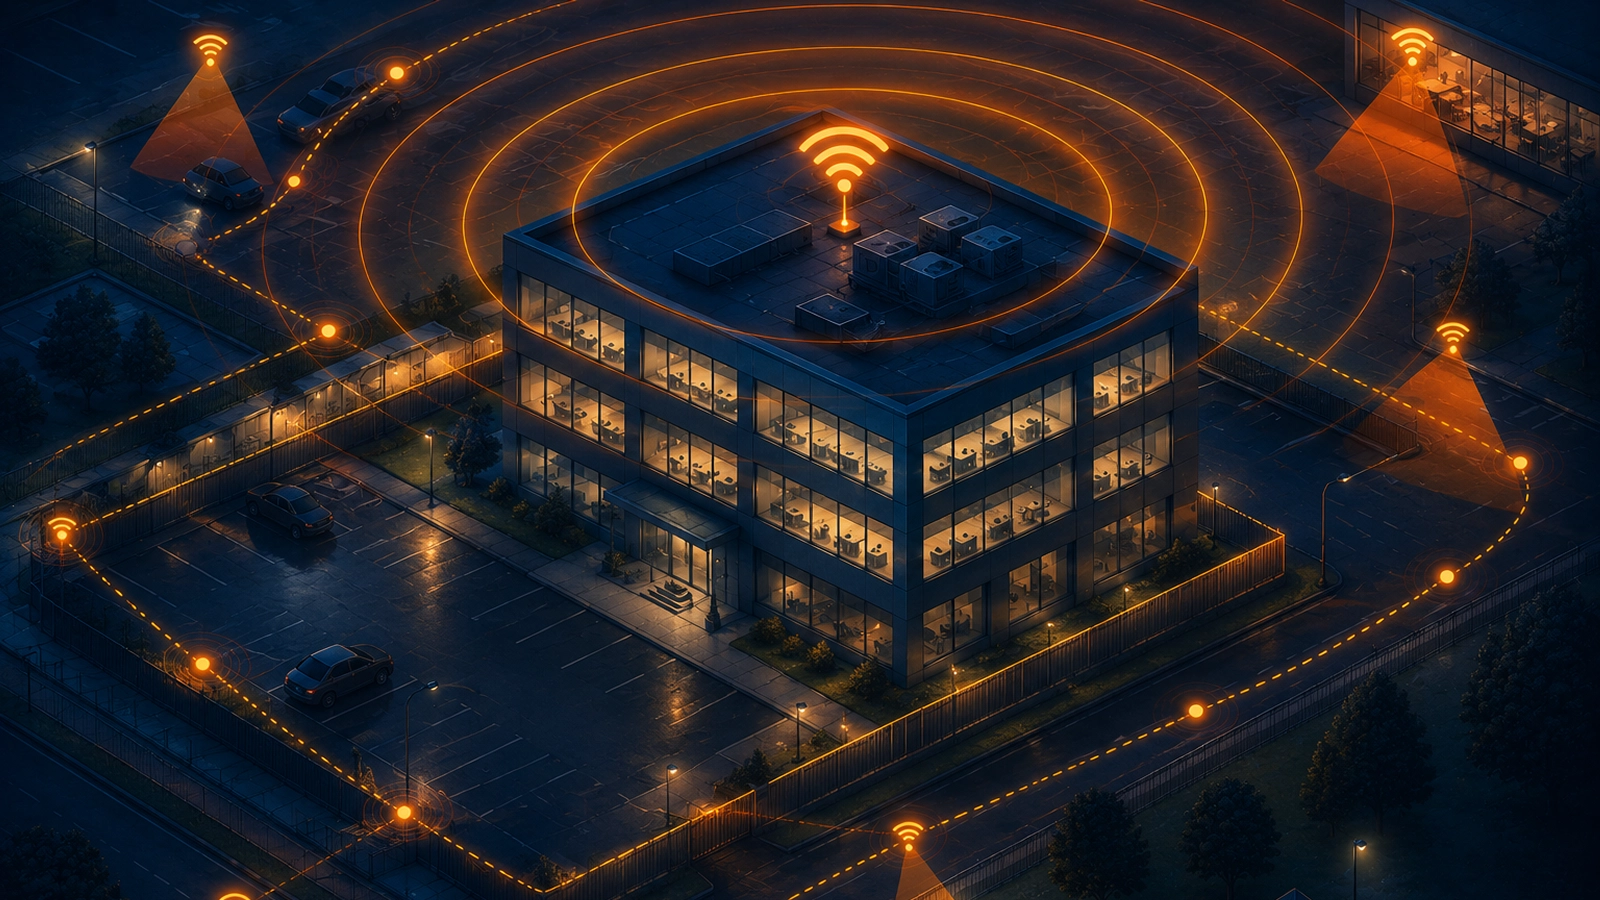
Signal Testing Happens Outside Your Walls Too
Testing doesn't stop at the front door. A tester walks the building's perimeter, the parking lot, and adjacent common areas, mapping exactly how far your signal reaches and what's accessible from each position.
Findings include a coverage map showing where signal strength allows a realistic attack attempt. The engagement also delivers a Risk Impact Brief for leadership, a Technical Pentest Report for your security team, and an Attestation Letter for your auditor, giving your facilities team concrete input for access point placement and shielding decisions.
Common Questions About Wireless Penetration Testing
Does testing cover our guest network?
Yes. Wireless penetration testing evaluates guest network segmentation directly, confirming whether guest traffic stays fully isolated from internal systems and sensitive data.
Does this cover WPA3 as well as WPA2?
Yes, testing covers WPA3 as well as WPA2. Testing assesses WPA2 configurations for resistance to handshake and PMKID cracking attempts, and checks WPA3 networks for fallback exposure, since most WPA3 deployments run in mixed mode to support older devices and can be forced back to WPA2.
Will testing include rogue access point detection?
Yes. Testing identifies unauthorized access points impersonating your network name and evaluates whether your current monitoring would detect one appearing on your premises.
Does wireless testing support PCI DSS compliance requirements?
Yes. Wireless testing can support PCI DSS Requirement 11.2.1 by identifying authorized and unauthorized wireless access points at least every three months, and Requirement 11.2.2 by supporting an inventory of authorized wireless access points with documented business justification.
Does testing cover every office location, or a representative sample for organizations with multiple sites?
Wireless testing scope is defined during the scoping call based on your organization's footprint. Multi-site organizations can choose full coverage across every location or a representative sample of sites that reflects your typical network configuration.
How long does wireless testing take?
Active testing typically runs one to two weeks depending on your site count and footprint, with the full engagement timeline, from scoping to final report, running longer.