A CMMC Level 1 self-assessment is an annual evaluation of the basic safeguarding requirements for Federal Contract Information (FCI). For organizations subject to Level 1, the assessment results must be entered into the Supplier Performance Risk System (SPRS), along with the required annual affirmation of compliance. As of July 13, 2026, Level 1 self-assessment requirements remain in place even though CMMC Phase 2 has been suspended.
This guide walks you through the CMMC Level 1 SPRS submission process, from confirming your assessment scope and completing the 15 applicable security requirements to preparing the required information, accessing SPRS, entering your results, and maintaining your record. It also covers common submission mistakes and what to expect after your assessment is recorded.
Also Read: CMMC Level 1 vs Level 2, Which Applies to You?
What You Need Before Starting Your SPRS Submission
Before entering a CMMC assessment into the Supplier Performance Risk System (SPRS), make sure your assessment scope, CMMC level, and supporting information are finalized. For Level 1, the organization conducts the self-assessment annually, enters the results into SPRS, and submits the required affirmation. The CMMC UID generated by SPRS is tied to the contractor information system that processes, stores, or transmits FCI or CUI.
Have these items ready:
- CMMC Level: Confirm the level required by the applicable solicitation or contract.
- Assessment Scope: Identify each contractor information system covered by the assessment and the FCI or CUI it handles.
- Assessment Results: Complete the applicable assessment before entering the results into SPRS.
- CMMC UID: Be prepared to associate the submission with the UID generated for each applicable system.
- CAGE Code: Keep the relevant organizational and system identification information available.
- Assessment Date: Record the date on which the assessment was completed.
- Assessment Score/Status: Ensure the information entered accurately reflects the completed assessment.
- Affirmation: For CMMC, the required affirmation must be submitted in SPRS after the assessment and maintained as required. Level 1 requires an annual assessment and affirmation.
The CMMC Level 1 SPRS Submission Process
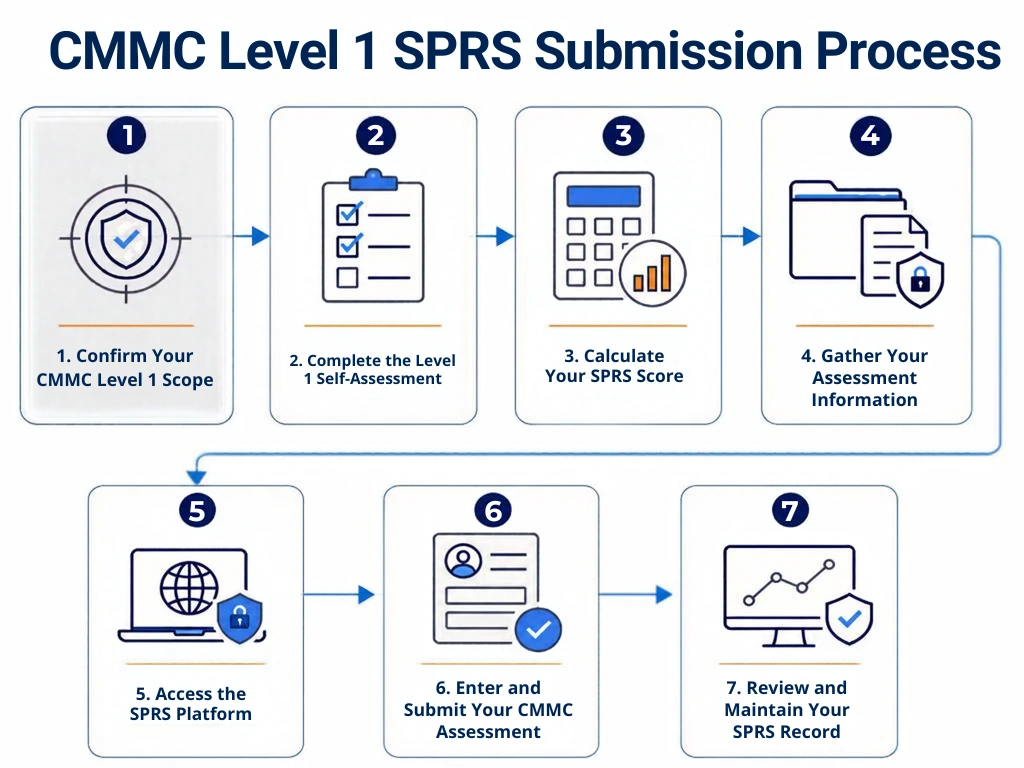
Submitting a CMMC Level 1 self-assessment in SPRS is more than entering a score. Organizations need to establish the correct assessment scope, complete the 15 Level 1 requirements, document the assessment accurately, and maintain the resulting CMMC status and annual affirmation. The current DoW framework requires Level 1 organizations to conduct a self-assessment annually, enter the results into SPRS, and maintain an affirmation of continuous compliance.
Step 1: Confirm Your CMMC Level 1 Scope
Start by identifying the contractor information system or systems that process, store, or transmit FCI under the applicable contract. Level 1 can apply to an entire enterprise network or to a defined enclave, depending on where FCI is handled. Establishing this boundary before the assessment helps ensure that the self-assessment covers the systems that actually fall within scope. Document the relevant systems, users, applications, network boundaries, and FCI flows. If multiple CMMC UIDs are needed, keep the scope for each system clearly documented because SPRS associates a CMMC UID with the applicable contractor information system.
Step 2: Complete the Level 1 Self-Assessment
Assess the in-scope environment against all 15 CMMC Level 1 security requirements from FAR 52.204-21. New solicitations may cite FAR 52.240-93 for the same 15 requirements. The assessment should establish whether each requirement is implemented, using the appropriate examination, interview, and testing methods described in the CMMC Level 1 Assessment Guide. Before moving to SPRS, make sure the assessment is complete and that the supporting evidence is organized. Level 1 does not permit POA&Ms, and the required status for award is Final Level 1 (Self), so unresolved requirements cannot simply be carried forward as a Level 1 POA&M.
Step 3: Confirm All 15 Requirements Are Met
For a CMMC Level 1 submission, the important outcome is establishing whether all 15 requirements have been satisfied. Unlike the NIST SP 800-171 scoring approach commonly associated with Level 2 assessments, Level 1 is based on the 15 FAR 52.204-21 requirements and results in a Final Level 1 (Self) status when the requirements are met.. Before entering information into SPRS, reconcile your assessment results with your evidence and confirm that the scope, assessment date, CMMC level, and status information are accurate. This reduces the risk of submitting information that does not accurately represent the assessed environment.
Step 4: Gather Your Assessment Information
Have the information needed for the SPRS record ready before beginning the submission. This includes the organization's identifying information, applicable CAGE Code, assessment scope, assessment date, CMMC level, and information associated with the contractor information system being assessed. You should also have the assessment results and supporting records available internally. The CMMC UID is assigned through SPRS for each CMMC assessment and is associated with the applicable contractor information system.
Step 5: Access the SPRS Platform
CMMC assessment information is entered through the Supplier Performance Risk System (SPRS), which is accessed through the Procurement Integrated Enterprise Environment (PIEE). The SPRS workflow includes the option to add a new CMMC Level 1 Self-Assessment and complete the subsequent affirmation process. Before starting, make sure you have the SPRS Cyber Vendor User role in PIEE and that your organization's Contractor Administrator has approved the role. This access is required to view and use the CMMC assessment entry screens in SPRS. If your organization manages more than one applicable CMMC assessment or system, carefully verify that you are working with the correct company and assessment record.
Step 6: Enter and Submit Your CMMC Assessment
After accessing SPRS through PIEE, navigate to Cyber Reports, select the CMMC Assessments tab, and choose Add New Level 1 CMMC Self-Assessment. Enter the assessment information carefully, including the assessment date, scope, CAGE information, CMMC level, and applicable contractor information system. If the person entering the assessment is not the organization's Affirming Official, the assessment record is transferred to the Affirming Official by email. The record remains Pending Affirmation until the Affirming Official reviews and certifies it.
Step 7: Review and Maintain Your SPRS Record
Submitting the assessment is not the end of the process. For Level 1, the resulting Final Level 1 (Self) status must remain current, and the affirming official must maintain the required annual affirmation of continuous compliance in SPRS. Current DFARS language defines Final Level 1 status as not older than one year, with a corresponding affirmation also not older than one year.
Common Mistakes to Avoid When Submitting in SPRS
A SPRS submission can become problematic when the information entered does not accurately match the completed CMMC assessment. Common mistakes include using the wrong assessment scope, entering incorrect organization details or assessment dates, confusing multiple CMMC UIDs, or submitting information before the Level 1 self-assessment is complete. Since contracting officers use SPRS to verify the required CMMC status associated with an applicable CMMC UID, accuracy is important throughout the submission process.
Organizations should also avoid treating submission as the final step in compliance. Level 1 requires an annual self-assessment and affirmation, and the resulting status needs to remain current. Reviewing the assessment scope, CMMC UID, organization information, assessment details, and affirmation before submission can help prevent inconsistencies that may create issues during contract award or other applicable contract actions.
Moving Ahead
Submitting a CMMC Level 1 self-assessment in SPRS is a straightforward process when the scope, assessment results, organizational details, and CMMC UID are verified before submission. The process does not end once the record is entered. Keeping assessment information accurate, maintaining the required annual affirmation, and reviewing changes to the in-scope environment can help organizations keep their CMMC status current and remain prepared for applicable DoW contract requirements.
Also Read: What CMMC Means for DoD Subcontractors