CMMC Level 1 remains at the foundational cybersecurity level for defense contractors that handle Federal Contract Information (FCI). In 2026, understanding what applies has become especially important as the Department of War suspended the planned Phase 2 requirements on July 13, 2026, while keeping Phase 1 self-assessment requirements in place. 32 CFR 170.15 establishes the Level 1 self-assessment requirements.
This guide breaks down the CMMC Level 1 requirements in 2026, explains the clause renumbering and what it means for contractors, clarifies the current status of Phase 2, and outlines the assessment and affirmation expectations that still apply. It also helps distinguish Level 1 requirements from Level 2 obligations, so organizations can understand which requirements are relevant to their contracts and information environment.
Also Read: What Is CMMC and Do You Need It?
CMMC Clause Renumbering: What Changed in 2026?
For solicitations issued on or after February 1, 2026, CMMC-related contract clauses were renumbered under the new FAR Part 40 structure. FAR 52.204-21 became FAR 52.240-93, and DFARS 252.204-7020 became DFARS 252.240-7997. Contractors reviewing older CMMC documentation or current 2026 solicitations may therefore see different clause numbers referring to requirements they already recognize.
The renumbering should not be treated as a simple "find and replace" exercise. Teams working across older and current contract documents should verify which clause applies to the solicitation or contract and confirm that each reference maps correctly before updating policies, SSPs, assessment evidence, remediation trackers, or internal control matrices.
Renumbering should not be treated as a simple "find and replace" exercise. Teams using older policies, SSPs, assessment evidence, remediation trackers, or internal control matrices should verify that each legacy reference maps correctly to the applicable CMMC 2.0 requirement.
The 15 CMMC Level 1 Security Requirements
CMMC Level 1 focuses on the basic safeguarding of Federal Contract Information (FCI). The requirements cover access control, identification and authentication, media and physical protection, system and communications protection, and system and information integrity.
- Limit System Access: Limit information system access to authorized users, processes acting on behalf of users, and authorized devices.
- Limit System Access to Authorized Functions: Restrict users to the transactions and functions they are authorized to perform.
- Control External Connections: Verify and control connections to external information systems to reduce unauthorized access.
- Control Publicly Accessible Information: Review publicly accessible information to ensure FCI is not improperly disclosed.
- Identify System Users, Processes, and Devices: Identify users, processes acting on behalf of users, and devices before granting access.
- Authenticate Identities: Authenticate users, processes, and devices before allowing them to access organizational systems.
- Sanitize or Destroy Media: Sanitize or destroy system media containing FCI before disposal or reuse to prevent unauthorized disclosure.
- Limit Physical Access: Limit physical access to systems, equipment, and operating environments to authorized individuals.
- Manage Visitors and Physical Access Devices: Escort visitors, monitor their activity, maintain physical access records, and manage physical access devices.
- Protect Communications at System Boundaries: Monitor, control, and protect communications at external and key internal system boundaries.
- Separate Publicly Accessible System Components: Physically or logically separate publicly accessible system components from internal networks.
- Identify and Correct System Flaws: Identify, report, and correct information system flaws in a timely manner.
- Protect Against Malicious Code: Deploy malicious code protection at appropriate locations within the information system.
- Update Malicious-Code Protection: Update malicious-code protection mechanisms whenever new releases are available in accordance with organizational requirements.
- Perform System and File Scans: Conduct periodic system scans and real-time scanning of files from external sources when downloaded, opened, or executed.
Also Read: How to Complete Your CMMC Level 1 Self-Assessment
CMMC Phase 2 Changes and What They Mean for Level 1
CMMC Phase 2 was originally scheduled to begin on November 10, 2026, introducing additional CMMC requirements into applicable DoW contracts. However, on July 13, 2026, the Department of War suspended the transition to Phase 2 and announced a broader review of the CMMC program. The change does not remove current Level 1 obligations. Phase 1 self-assessment requirements remain in place.
For Level 1 organizations, the practical impact is therefore limited. Organizations handling FCI must continue meeting the 15 FAR 52.204-21 security requirements, completing an annual self-assessment, entering the results into SPRS, and submitting the required annual affirmation. POA&Ms are not permitted at Level 1.
Moreover, Level 1 organizations should do the following things now:
- The Phase 2 suspension does not eliminate the existing Level 1 requirements.
- Maintain documentation supporting implementation of the 15 requirements.
- Level 1 remains an annual self-assessment obligation.
- CMMC requirements apply through applicable DoW contracts, so organizations should review the requirements attached to their contracts.
- The Department has established a reform effort, so organizations should avoid treating the previously announced Phase 2 timeline as the current schedule.
The key takeaway for Level 1 organizations is simple: Phase 2 is currently suspended, but Level 1's compliance continues. Teams should maintain their existing safeguards and assessment processes while following official CMMC updates for future changes.
What CMMC Level 1 Requires in 2026
CMMC Level 1 focuses on the basic safeguarding of Federal Contract Information (FCI) and includes 15 security requirements from FAR 52.204-21. For applicable contracts, organizations must maintain the required safeguards and achieve a Final Level 1 (Self) status.
| Requirement | What It Means in Practice |
|---|---|
| 15 Level 1 Requirements | Implement the basic safeguarding requirements covering access, authentication, physical protection, communications, and system integrity. |
| Annual Self-Assessment | Assess the applicable contractor information system against the Level 1 requirements each year. |
| SPRS Submission | Enter the self-assessment results into the Supplier Performance Risk System (SPRS). |
| Annual Affirmation | An affirming official must attest to continuing compliance annually. |
| Final Status | Level 1 requires a current Final Level 1 (Self) status; conditional status is not available at Level 1. |
| POA&M | Plans of Action and Milestones are not permitted for Level 1. |
The scope is also important: Level 1 assessment applies to the systems and assets that process, store, or transmit FCI, rather than automatically applying to every system across the organization. In 2026, the practical focus remains maintaining these safeguards and keeping the annual assessment and affirmation current. DoW's July 2026 suspension of CMMC Phase II does not remove the Phase I Level 1 self-assessment requirements.
Also Read: The DoD Suspended CMMC Phase 2: What It Means for Your Business
CMMC Level 1 vs. Level 2: Which One Applies to You?
The most important distinction is the type of information your organization handles under the applicable DoW contract. CMMC Level 1 focuses on Federal Contract Information (FCI) and includes 15 requirements from FAR 52.204-21. Level 2 focuses on Controlled Unclassified Information (CUI) and incorporates 110 requirements from NIST SP 800-171 Rev. 2.
| Factor | CMMC Level 1 | CMMC Level 2 |
|---|---|---|
| Information Protected | FCI | CUI |
| Security Requirements | 15 FAR 52.204-21 requirements | 110 NIST SP 800-171 Rev. 2 requirements |
| Assessment | Annual self-assessment | Self-assessment every 3 years for applicable programs; C3PAO assessment where required |
| Affirmation | Annual | Annual |
| POA&M | Not permitted | Permitted under defined conditions |
| Security Depth | Basic safeguarding | Broader protection for CUI |
For organizations deciding between the two, data type and the specific contract requirement should drive the decision, rather than company size or industry alone. During the current CMMC Phase 2 suspension, DoW states that Phase 1 self-assessment requirements remain in place.
How to Prepare for CMMC Level 1 Compliance in 2026
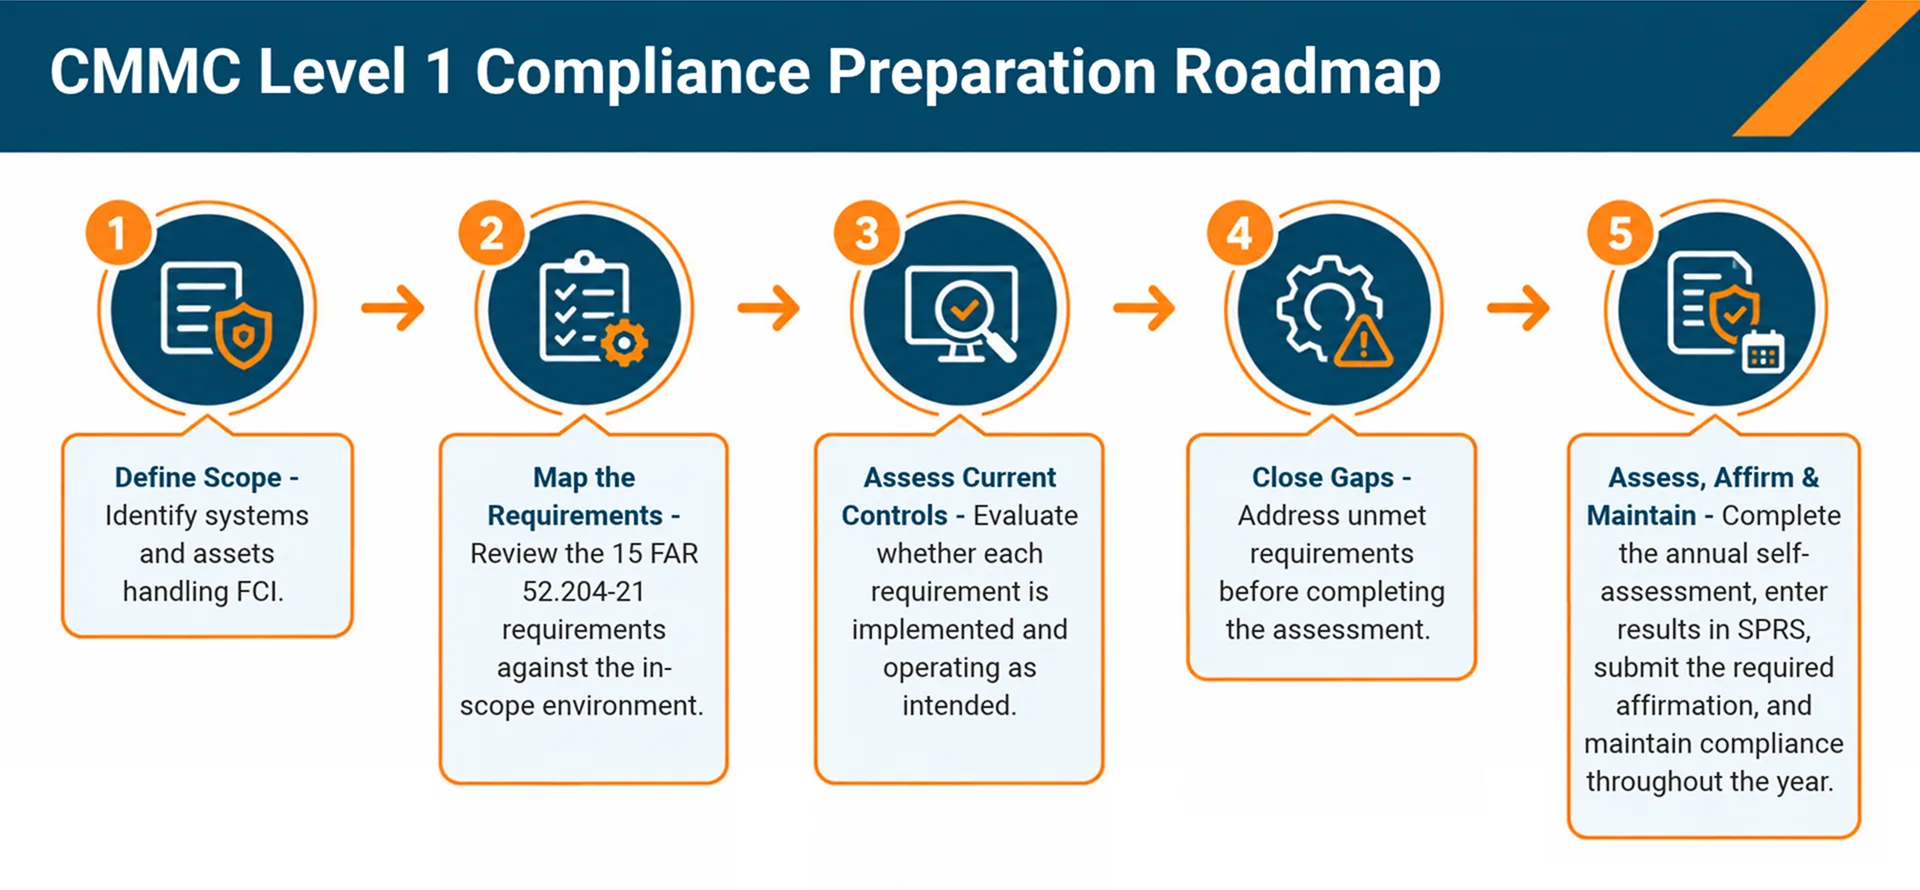
Preparing for CMMC Level 1 starts with defining which systems and assets process, store, or transmit Federal Contract Information (FCI). Organizations then assess those in-scope assets against the 15 Level 1 requirements, address any gaps, document the results, and complete the required annual self-assessment and affirmation in SPRS. Level 1 does not permit POA&Ms, so all requirements need to be satisfied for a Final Level 1 (Self) status.
Moving Ahead
CMMC Level 1 in 2026 is less about preparing for a one-time assessment and more about maintaining consistent protection for FCI throughout the year. With 15 requirements, annual self-assessment, SPRS reporting, and annual affirmation, organizations need clear ownership and reliable evidence of implementation. Keeping scope, controls, and evidence aligned makes the assessment process more manageable while helping organizations stay prepared as DoW continues to review and evolve the CMMC program.